跟进:良品计划社长清水智为无印良品信息泄露致歉:承认约109万件卡号未加密保存、本应删除
运营「无印良品」的日本良品计划公司社长清水智 11 月 12 日在东京举行记者会,就旗下应用与网店遭非法访问、客户信息可能外泄一事公开致歉。他承认,约 109 万件 MUJI Card 信用卡的完整卡号在应当删除后仍被保留,且保存时既未屏蔽也未加密,是公司数据运用管理上的疏漏。
良品计划此前分四次通报此事:10 月 30 日第一报称官方应用遭未授权访问、最多约 2,726 万件客户信息可能受影响;11 月 4 日第二报确认约 109 万件 MUJI Card 卡号全桁可能被外部访问。清水智在记者会上说明,2021 年 7 月之前,公司一直用卡号识别 MUJI Card 会员并给予专属优惠;该月更换积分系统后,本应停止取得并删除卡号,实际却没有删除。涉事卡由 Credit Saison 发行,其中约 34.5 万张目前仍在有效期内。
11 月 9 日的第四报又披露新情况:11 月 7 日检出的清单型攻击可能使约 27 万件购买记录外泄;2020 年 1 月至 2025 年 2 月货到付款的收件人信息约 44 万件也被新纳入可能受影响范围,含姓名、住址等信息的数据由约 52 万件上修至约 75 万件。无印良品网店自 11 月 6 日起暂停,恢复时间未定;恢复时将要求全体用户重设密码。
良品计划表示,将承担涉事 MUJI Card 换发新卡的手续费,并自 11 月 10 日起通过邮件与邮寄逐一联系受影响客户。无印良品中国 11 月 6 日曾说明,中国消费者信息经核查确认安全、与此次日本发生的事件无关。
关联:良品计划第二报:无印良品约109万件MUJI Card卡号全桁可能被外部访问、2726万件会员信息受影响
(来源:共同社)
Follow-Up: Ryohin Keikaku President Satoshi Shimizu Apologizes Over MUJI Data Breach, Admitting About 1.09 Million Card Numbers Were Kept Unencrypted and Should Have Been Deleted
Satoshi Shimizu, president of Ryohin Keikaku, the Japanese company that operates MUJI, apologized at a Tokyo press conference on November 12 over the unauthorized access to the brand's app and online store that may have exposed customer information. He admitted that the full card numbers of about 1.09 million MUJI Card credit cards were retained after they should have been deleted, and were stored without masking or encryption, calling it a failure in the company's data management.
Ryohin Keikaku has issued four updates on the incident. Its first report, on October 30, said the official app had been accessed without authorization and that up to about 27.26 million customer records could be affected; the second report, on November 4, confirmed that the full numbers of about 1.09 million MUJI Card accounts might have been accessed externally. Shimizu explained that until July 2021 the company used card numbers to identify MUJI Card members and grant them benefits; after the rewards system changed that month, the numbers should have stopped being collected and been deleted, but they were not. The cards were issued by Credit Saison, and about 345,000 of them are still valid.
The fourth report, on November 9, added new findings: a credential-stuffing attack detected on November 7 may have exposed about 270,000 purchase-history records, and roughly 440,000 cash-on-delivery recipient records from January 2020 to February 2025 were newly included in the possible scope, raising records containing names and addresses from about 520,000 to about 750,000. MUJI's online store has been suspended since November 6, with no date set for reopening; all users will be required to reset their passwords when it reopens.
The company said it will bear the cost of reissuing affected MUJI Cards and began notifying affected customers by email and post on November 10. MUJI China said on November 6 that Chinese consumer information had been checked and confirmed safe, and was unrelated to the incident in Japan.
(Source: Kyodo News)
来源:共同社
发布:GSM·美国(发布链接)
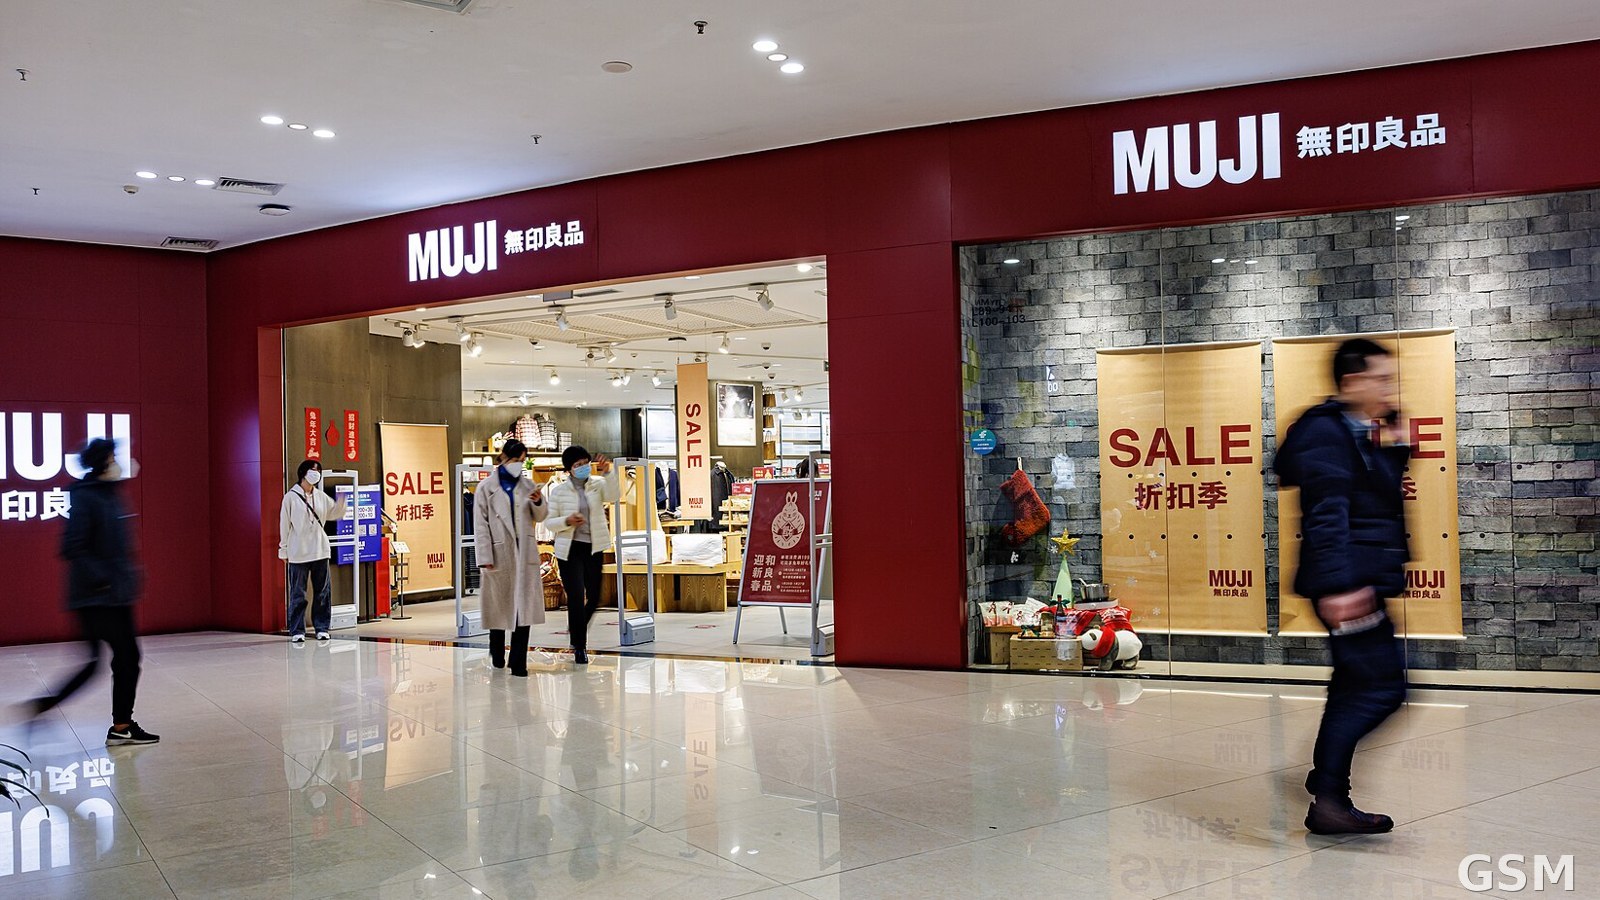
图片来源:图:一家无印良品门店(CC BY-SA 4.0,经 Wikimedia Commons)。 / Photo: A MUJI store (CC BY-SA 4.0, via Wikimedia Commons).
GSM Global · 本篇英文版 English edition of this story