良品计划第二报:无印良品约109万件MUJI Card卡号全桁可能被外部访问、2726万件会员信息受影响
东京——运营无印良品(MUJI)的日本零售商良品计划11月4日发布第二报称,其官方应用遭外部非法访问一事影响范围扩大:由 Credit Saison 发行的联名信用卡「MUJI Card」约109万件会员记录中,信用卡号的全部桁数可能已被外部访问,其中仍有效的卡约34.5万件。良品计划10月30日发布第一报时曾称信用卡信息不在受影响之列,第二报推翻了这一说法。
第一报称,包括已退会者在内,最多约2726万件会员记录的电子邮箱地址、出生日期、性别与会员ID可能被外部访问。第二报确认,受影响范围不限于官方应用的用户,还包括无印良品网络商店的会员;其中约52万件记录还包括姓名、住所与电话号码。
MUJI Card 部分针对2021年7月之前入会的会员:可能被访问的是卡号全桁、MUJI Card ID 与出生日期,持卡人姓名、卡片有效期与安全码不在其中。在约34.5万件仍然有效的卡中,约16.8万件还与电子邮箱地址等信息一并处于可被阅览的状态。另有约120件在官方应用或网络商店登记过的信用卡记录,卡号前6位与后2位以及持卡人姓名可能被访问。
这些卡号为何在联动结束多年后仍留存在良品计划的系统里?据公司说明,2021年7月以前,公司为进行会员判定与积分发放,会取得 MUJI Card 入会者的卡号等信息;相关联动在2021年7月结束、现行系统已不再保存,但旧数据没有被删除、一直残留,且保护不充分。公司表示,这是自身的疏漏。
良品计划称,外部非法访问目前已被阻断,官方应用与网络商店照常营业,截至第二报发布时,尚未确认有信息流出至暗网、也未确认出现冒用信息造成的损失。发卡方 Credit Saison 表示,未确认其自身系统遭到非法访问,已加强对不正当使用的监控,持卡人可联系该公司申请换发新卡。良品计划提醒,公司不会通过电子邮件或电话向顾客索要信用卡信息,呼吁用户对可疑联系保持警惕。
MUJI Operator's Second Report: Full Card Numbers of About 1.09 Million MUJI Card Members May Have Been Accessed, With Up to 27.26 Million Accounts Affected
Tokyo — Ryohin Keikaku, the Japanese retailer that operates MUJI, said in a second report on November 4 that the scope of an unauthorized external access incident involving its official app had widened: for about 1.09 million records of the MUJI Card co-branded credit card issued by Credit Saison, the full card numbers may have been accessed from outside, including about 345,000 cards that remain valid. The company's first report on October 30 had said credit card information was not affected; the second report reversed that statement.
The first report said that for up to about 27.26 million member records, including those of former members, email addresses, dates of birth, gender and member IDs may have been accessed. The second report confirmed that the scope was not limited to users of the official app but also included members of the MUJI online store, and that for about 520,000 of the records, names, addresses and telephone numbers were also involved.
The MUJI Card portion covers members who joined by July 2021: the full card number, the MUJI Card ID and the date of birth may have been accessed, while cardholder names, expiration dates and security codes were not included. Of the roughly 345,000 cards still valid, about 168,000 were in a state where they could be viewed together with information such as email addresses. For about 120 further records of cards registered through the app or the online store, the first six and last two digits of the card number and the cardholder name may have been accessed.
Why did the numbers remain in Ryohin Keikaku's systems years after the data link ended? According to the company, before July 2021 it obtained the card numbers and related data of MUJI Card members in order to verify membership and award points. That linkage ended in July 2021 and the current system no longer stores the data, but the old data was never deleted, remained in the system, and was not adequately protected. The company said this was a deficiency on its part.
Ryohin Keikaku said the unauthorized access had now been blocked, the official app and online store were operating as usual, and that as of the second report it had confirmed no leak of the information to the dark web and no damage from misuse. Credit Saison said it had found no unauthorized access to its own systems, had stepped up monitoring for fraudulent use, and that cardholders could contact it to have a card reissued. Ryohin Keikaku reminded customers that it never asks for credit card information by email or telephone and urged vigilance against suspicious contacts.
来源:良品计划
发布:GSM·美国(发布链接)
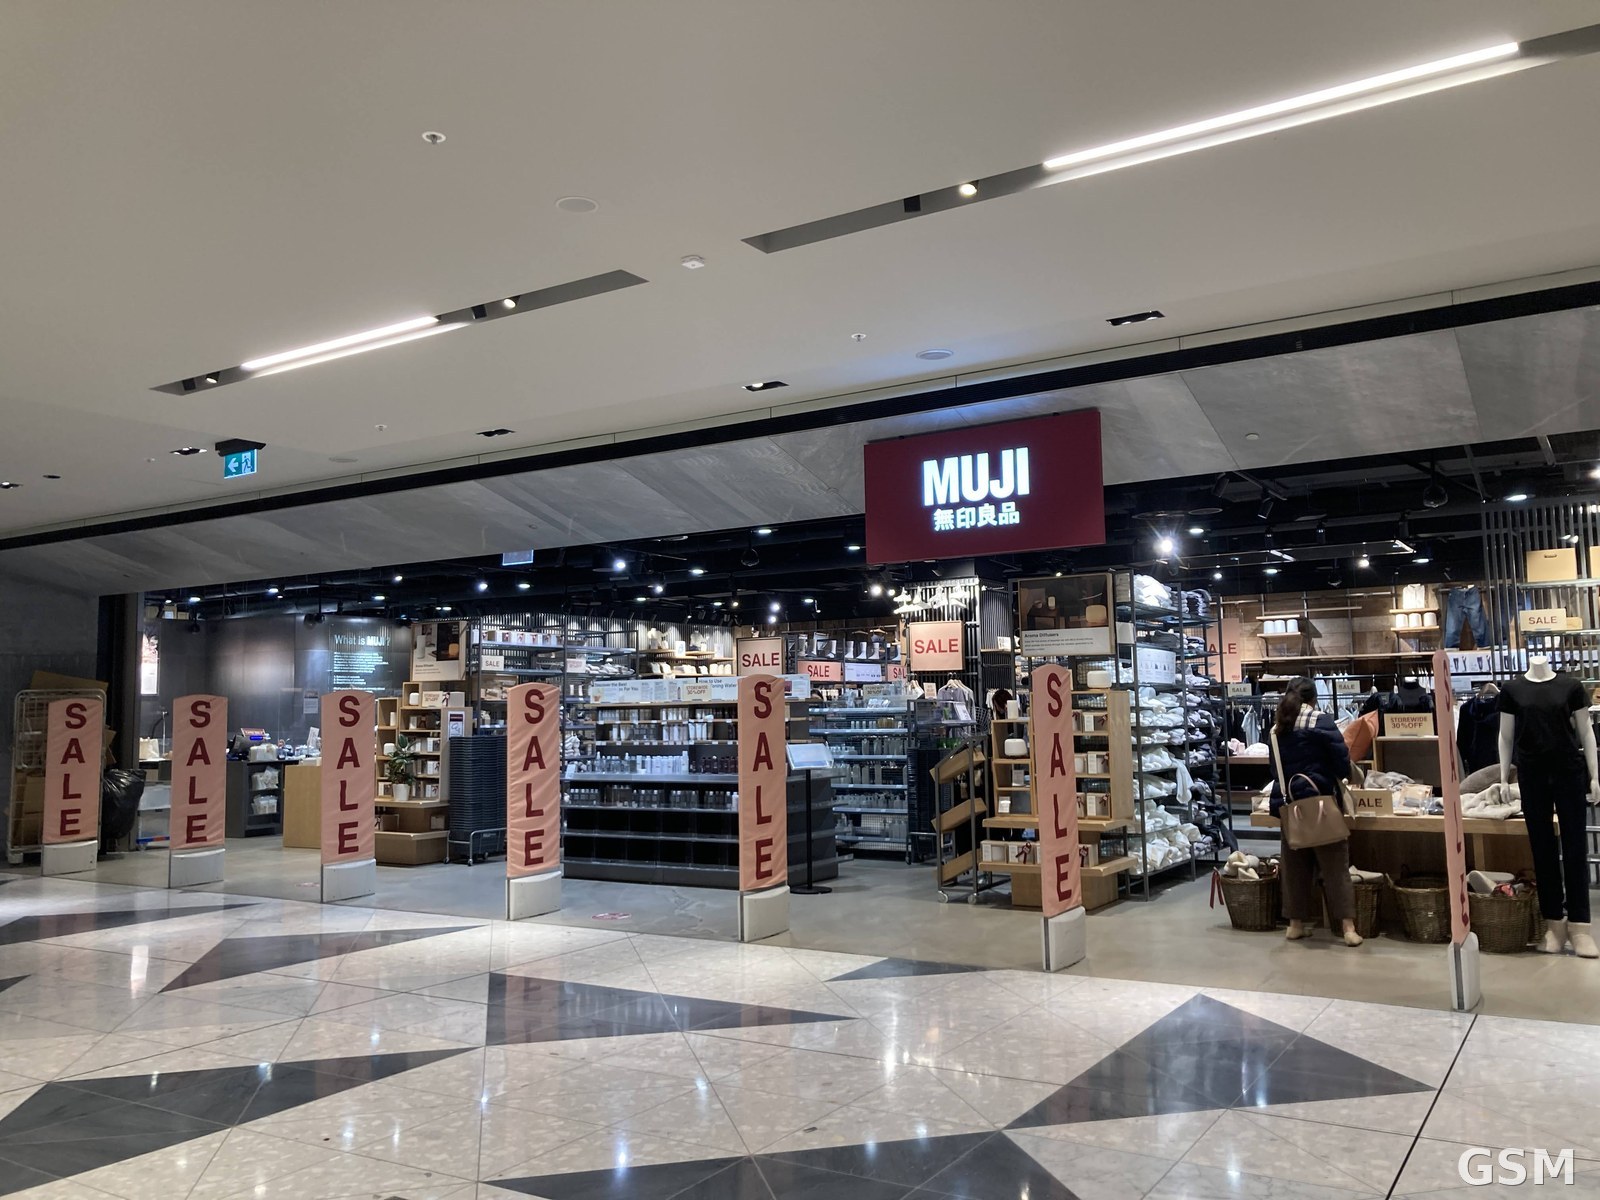
图片来源:图:一家无印良品(MUJI)门店。照片 CC BY-SA 4.0(Nick-D),经 Wikimedia Commons。 / Photo: A MUJI store. CC BY-SA 4.0 (Nick-D), via Wikimedia Commons.
GSM Global · 本篇英文版 English edition of this story