跟进:欧洲七国超市冷柜再遭网络攻击 柜温升至50摄氏度大量食品报废
11月2日凌晨,欧洲七国超市制冷系统再遭网络攻击:攻击者远程把联网冷柜、冷冻柜的蒸发器切换到除霜模式,部分柜内温度升至50摄氏度,逾115家门店受影响,大量变质的冷藏、冷冻食品被整批丢弃。这是三周内第二波针对超市制冷系统的攻击——10月,法国约700家超市曾遭同类攻击。随着各国机构、涉事企业与监管部门陆续披露细节,事件的完整图景、美国的一条并行调查线,以及这类设备早已公开的漏洞,也逐渐清晰。
运营 Delhaize 制冷系统的比利时公司 Sabcobel 负责人 Stephan Moelans 对 Belga 通讯社说,这是一起网络攻击,受攻击机组的蒸发器被远程切换到除霜模式,公司技术人员从凌晨1点起连夜把受影响设备逐台断网。瑞典 ICA 在斯德哥尔摩的一家加盟店说,攻击发生在凌晨2点、数小时后才被发现,店内全部冷冻柜升至50摄氏度,销售经理 Engla Ingwall 说:「全毁了。」
比利时和卢森堡是重灾区。荷兰零售集团 Ahold Delhaize 称,连夜发生的「IT事件」影响了旗下 Delhaize 在比利时与卢森堡数十家门店的冷柜与冷冻柜,多家欧洲媒体估计受影响的 Delhaize 门店约40家;发言人 Sarah De Meester 说,公司周一发现制冷系统温度上升,正在调查。宜家在比利时 Mons 的一家门店也中招。安特卫普以南 Hove 的一家肉铺连锁门店冷柜被升至18摄氏度,创始人 Luc De Laet 说,约1.5万欧元的肉品报废。据 BBC 报道,布鲁塞尔近郊 Hoeilaart 的一家 Delhaize 门店估计损失超过10万欧元。比利时媒体汇总各连锁的通报,该国受影响门店合计约60家。
瑞典 Coop 确认,旗下800家门店中有7家的制冷系统遭未经授权的篡改,并证实是网络事件,丹麦制冷设备商 Danfoss 是其供应商之一。ICA 称少数门店的冷藏、冷冻系统连夜出事,其位于瑞典南部 Sjöbo 的一家 ICA Kvantum 门店在社交媒体上说,店内冷柜被黑客设定到50摄氏度。爱沙尼亚公共广播 ERR 报道,攻击者侵入制冷技术公司 Kitman Coldtech 一名客户的制冷控制电脑,把温度设定到50摄氏度。荷兰方面,Danfoss 对荷兰公共广播 NOS 说,荷兰至少17处使用其系统的设施在同一夜遭同类攻击,包括肉铺和冷冻仓储点。爱尔兰食品批发商 Musgrave 说,旗下13家 SuperValu 门店的制冷系统受网络事件影响,已把部分冷藏、冷冻商品下架,公司的监测系统发出警报后已立即处置,调查仍在进行。芬兰 Kesko 旗下门店也报告了同类故障。另有报道提到德国、葡萄牙、罗马尼亚和意大利也有门店出现同类问题,但尚未得到这些国家的官方或涉事企业确认。
欧盟委员会农业与食品委员 Christophe Hansen 说:「这是对我们食品供应链的蓄意破坏,也是对消费者信心的打击,这是一个必须严肃对待的警告。」他说:「这类网络攻击一再发生,令人深感忧虑。」比利时网络安全中心发言人 Katrien Eggers 说,目前尚不清楚幕后黑手是谁。瑞典国家网络安全中心负责人 John Billow 说,该中心正在处理瑞典国内多起相关事件,对攻击者身份不作猜测。截至目前,没有任何组织宣称对两波攻击负责,各国也未公开点名任何嫌疑方。
美国还有一条并行调查线。路透社10月29日报道,今年8月下旬,美国至少六家军事基地的军人商店(commissary)冷柜接连故障、大量食品变质,五角大楼已按疑似网络攻击调查,由国防刑事调查局牵头,美军调查人员正与法国执法部门联查;五角大楼当时并未证实确系黑客所为。据美国防务媒体 Nextgov/FCW 11月2日报道,两名知情人士称,美方官员怀疑幕后是与伊朗有关联的黑客,但这一判断没有公开证据,也可能随调查进展而变化。
这次攻击与10月11日夜间法国那次手法相同。当晚,法国各地超市的制冷控制器遭远程劫持;财政部长 Roland Lescure 随后对议会说,全国约1万家超市中约700家受影响。部分冷柜升至50摄氏度,除大量食品报废外还引发火情,路透社当时报道,估计损失达数千万欧元。巴黎检方已就这起「大规模网络攻击」立案调查,法国国家网络安全局 ANSSI 发布警示,指涉事控制器主要是 Danfoss 产品,另有 Copeland 与 Dixell 的系统,其中不少是已停止安全更新的老旧型号,却仍暴露在互联网上。
法国国家网络安全局(ANSSI)下属的 CERT-FR 已在10月12日发布编号 CERTFR-2026-ALE-012 的警示,并于10月13日、16日两度更新,点名四条受影响的控制器产品线:Danfoss AK-SM 系列、Danfoss AK-SC 系列、Copeland xweb 与 Dixell xweb。警示明确指出,把这类设备的管理介面直接暴露在互联网上「违反良好做法」;针对这些设备的攻击行动很可能仍在进行,已停止安全更新(EOL)的老旧型号若继续暴露在网上,被攻陷的概率极高,而且仅做恢复出厂设置并不够——那只能清掉攻击者的落脚点,设备本身依然脆弱。Danfoss 确认,法国受影响的机组中包括 AK-SM 800(2021年已停止支持)与 AK-SC 355(2016年已停产)等老型号。
这类设备的漏洞其实早有公开记录。今年8月,工业网络安全公司 Claroty 旗下的 Team82 团队公布了对 Danfoss AK-SM 800A 系统管理器的研究,并在拉斯维加斯 DEF CON 大会上作了演示:该设备的网页管理介面藏有一个按日期生成口令的「当日密码」登录机制,可绕过正常验证(编号 CVE-2025-41450),另有一条命令注入漏洞(CVE-2025-41451)与一条可致服务中断的配置注入漏洞(CVE-2025-41452);研究团队按 Censys 扫描数据统计,全球有2,765台这类设备的管理介面直接暴露在互联网上。Danfoss 已发布 R4.3.1 版固件,修复这三条漏洞。不过,调查方迄今没有确认法国与本轮攻击究竟是利用了哪一条漏洞入侵。
周一受影响的机组中,至少一部分使用 Danfoss 技术,该公司的设备在法国那次攻击中同样是目标;Danfoss 说,公司正与客户合作落实修复。网络安全公司 SentinelOne 研究员 Tom Hegel 说,这类攻击通常与勒索、政治动机或国家行为有关,而近两起案件都没有出现索赎要求,更像是蓄意破坏。
损失由谁承担也成了问题。据保险业媒体《Insurance Business》报道,这类事件正好卡在两类保单的夹缝里:网络保险通常把实体损失排除在外,财产险中的食品变质保障又可能带有网络攻击除外条款;保险经纪公司 Lockton 指出,仅法国两家门店的库存损失就达27万欧元。运营 Delhaize 制冷系统的 Sabcobel 负责人还表示,受影响机组需要做硬件层面的改造,而不只是软件更新——对仍在用老旧控制器的商家来说,换机与改造都是一笔实打实的开支。
关联:五角大楼把8月多座基地冷柜故障按疑似网络攻击调查:至少6家军人商店食品变质,美方正与法国执法部门联查
关联:欧洲多国超市冷柜疑遭网攻:逾115家门店受影响,部分冷柜温度升至50摄氏度以上
(来源:路透社、美联社、法国CERT-FR)
Follow-up: Supermarket Fridges Hacked Across Seven European Countries, Temperatures Hit 50°C as Food Spoils
In the early hours of Monday, November 2, supermarket refrigeration systems in seven European countries were hit by another cyberattack: attackers remotely switched the evaporators of networked fridges and freezers into defrost mode, pushing temperatures inside some units to 50 degrees Celsius (122 degrees Fahrenheit), affecting more than 115 stores and forcing them to throw away large quantities of spoiled food. It was the second wave of such attacks in three weeks — in October, about 700 French supermarkets were hit. As authorities, companies and regulators disclosed more details, a fuller picture emerged, along with a parallel investigation in the United States and a set of long-public vulnerabilities in the equipment involved.
Stephan Moelans, head of Sabcobel, the Belgian company that operates Delhaize's refrigeration systems, told the Belga news agency it was a cyberattack: the evaporators of the affected units had been switched to defrost mode, and technicians had been disconnecting the installations from the network since 1 a.m. An ICA franchise store in Stockholm said the attack occurred at 2 a.m. but was only noticed hours later, with all of its freezers reaching 50 degrees. "Everything is destroyed," said Engla Ingwall, the store's sales manager.
Belgium and Luxembourg were hit hardest. Dutch retailer Ahold Delhaize said an overnight "IT incident" had affected the fridges and freezers of dozens of its Delhaize stores in Belgium and Luxembourg; European media put the number of affected Delhaize stores at around 40. Spokesperson Sarah De Meester said the chain detected the temperature rise in its cooling systems on Monday and was investigating. IKEA also had one store hit, in Mons, Belgium. A butcher chain store in Hove, south of Antwerp, had a freezer raised to 18 degrees; founder Luc De Laet said about 15,000 euros of meat was ruined. The BBC reported that a Delhaize store in Hoeilaart, near Brussels, estimated its losses at more than 100,000 euros. Belgian media, tallying the chains' reports, put the country's affected stores at about 60 in total.
In Sweden, Coop said 7 of its 800 stores had their cooling systems tampered with in a cyber incident, and that Danfoss, the Danish refrigeration equipment maker, was among its suppliers. ICA said a limited number of its stores were affected overnight; one ICA Kvantum store in Sjöbo, in southern Sweden, said on Facebook that its fridges and freezers had been hacked and set to 50 degrees. In Estonia, public broadcaster ERR reported that attackers had accessed a computer controlling a client's refrigeration system at technology firm Kitman Coldtech and raised the temperature to 50 degrees. In the Netherlands, Danfoss told public broadcaster NOS that at least 17 facilities using its systems, including butcher shops and frozen-product storage sites, were hit by an attack of the same kind overnight. In Ireland, food wholesaler Musgrave said a cyber incident had affected refrigeration systems in 13 of its SuperValu stores, forcing it to remove some chilled and frozen products from sale; its monitoring systems had alerted it to the problem and its investigation was ongoing. Stores run by Finland's Kesko also reported similar failures. There were also reports of similar problems at stores in Germany, Portugal, Romania and Italy, but these had not been confirmed by officials or companies in those countries.
Christophe Hansen, the European Commissioner for Agriculture and Food, said: "They are a deliberate attempt to disrupt our food supply chain and undermine consumers' confidence in it - a warning that we must take seriously." He added: "The repeated occurrence of these cyberattacks is deeply concerning." Katrien Eggers, spokesperson for Belgium's Centre for Cybersecurity, said it was not known who was behind the attack. John Billow, head of Sweden's national cybersecurity centre, said the centre was working on several incidents affecting grocery stores across the country and could not speculate on who was responsible. No group has claimed responsibility for either wave of attacks, and authorities have not publicly identified any perpetrator.
There is also a parallel line of investigation in the United States. Reuters reported on October 29 that the Pentagon is treating a string of late-August refrigeration failures at at least six U.S. military commissaries, which spoiled large quantities of food, as a suspected cyberattack, with the Defense Criminal Investigative Service leading the probe and U.S. investigators working with French law enforcement; the Pentagon has not confirmed that hackers were responsible. On November 2, the defense publication Nextgov/FCW reported that, according to two people familiar with the matter, U.S. officials suspect Iran-linked hackers were behind the intrusions - an assessment presented without public evidence that could change as the investigation proceeds.
The new attack used the same method as the one in France on the night of October 11. Hackers remotely seized control of refrigeration controllers at supermarkets across France; Finance Minister Roland Lescure later told lawmakers that about 700 of the country's roughly 10,000 supermarkets were affected. Temperatures in some units rose to 50 degrees, causing fires as well as heavy food losses, and Reuters reported at the time that losses were estimated in the tens of millions of euros. The Paris prosecutor's office opened an investigation into what it called a large-scale cyberattack, and France's cybersecurity agency ANSSI issued alerts identifying the affected controllers as mainly Danfoss products, along with Copeland and Dixell systems - many of them older, end-of-life models that no longer receive security updates but remained exposed to the internet.
CERT-FR, the response centre of France's national cybersecurity agency ANSSI, issued alert CERTFR-2026-ALE-012 on October 12 and updated it on October 13 and 16, naming four affected controller product lines: Danfoss's AK-SM series, Danfoss's AK-SC series, Copeland xweb and Dixell xweb. The alert states plainly that exposing the management interface of such equipment directly to the internet is contrary to good practice. It warned that attack campaigns against these devices were probably still under way, that end-of-life models left online faced a very high probability of compromise, and that a factory reset alone was not enough: it removes the attacker's foothold but leaves the device just as vulnerable. Danfoss confirmed that the units hit in France included legacy models such as the AK-SM 800, which went out of support in 2021, and the AK-SC 355, discontinued in 2016.
The flaws in this equipment were already on the public record. In August, Team82, the research arm of industrial cybersecurity firm Claroty, published a study of Danfoss's AK-SM 800A system manager and presented it at the DEF CON conference in Las Vegas: the device's web management interface contained a hidden 'code-of-the-day' login that derives a password from the current date and bypasses normal authentication (CVE-2025-41450), along with a command-injection flaw (CVE-2025-41451) and a configuration-injection flaw that can cause denial of service (CVE-2025-41452). From Censys scanning data, the researchers counted 2,765 of these management interfaces exposed directly to the internet. Danfoss has released firmware R4.3.1 fixing all three flaws. Investigators have not, however, confirmed which vulnerability, if any, was used to break into the systems in France or in this week's attacks.
At least some of the units hit on Monday used Danfoss technology that was also targeted in France, and the company said it had been working with customers to implement fixes. Tom Hegel, a researcher at cybersecurity firm SentinelOne, said such attacks were typically linked to extortion, political motives or nation-state operations, with the absence of financial demands in the recent cases pointing instead to sabotage.
Who bears the losses is also in dispute. Insurance Business magazine reported that the attacks fall into a gap between two kinds of cover: cyber policies often exclude physical loss, while property policies with spoilage cover may contain cyber exclusions. Broker Lockton has pointed to EUR270,000 in stock losses at just two French stores. The head of Sabcobel, which operates Delhaize's refrigeration systems, also said the affected units needed physical modifications, not just software updates - a real expense for retailers still running legacy controllers.
Related: Thousands of Supermarket Fridges Hacked Across France, Major Chains Hit
Related: Pentagon Treats August Freezer Failures at U.S. Bases as Suspected Cyberattack, Officials Say
(Source: Reuters, Associated Press, CERT-FR)
来源:路透社、美联社、法国CERT-FR
发布:GSM·美国(发布链接)
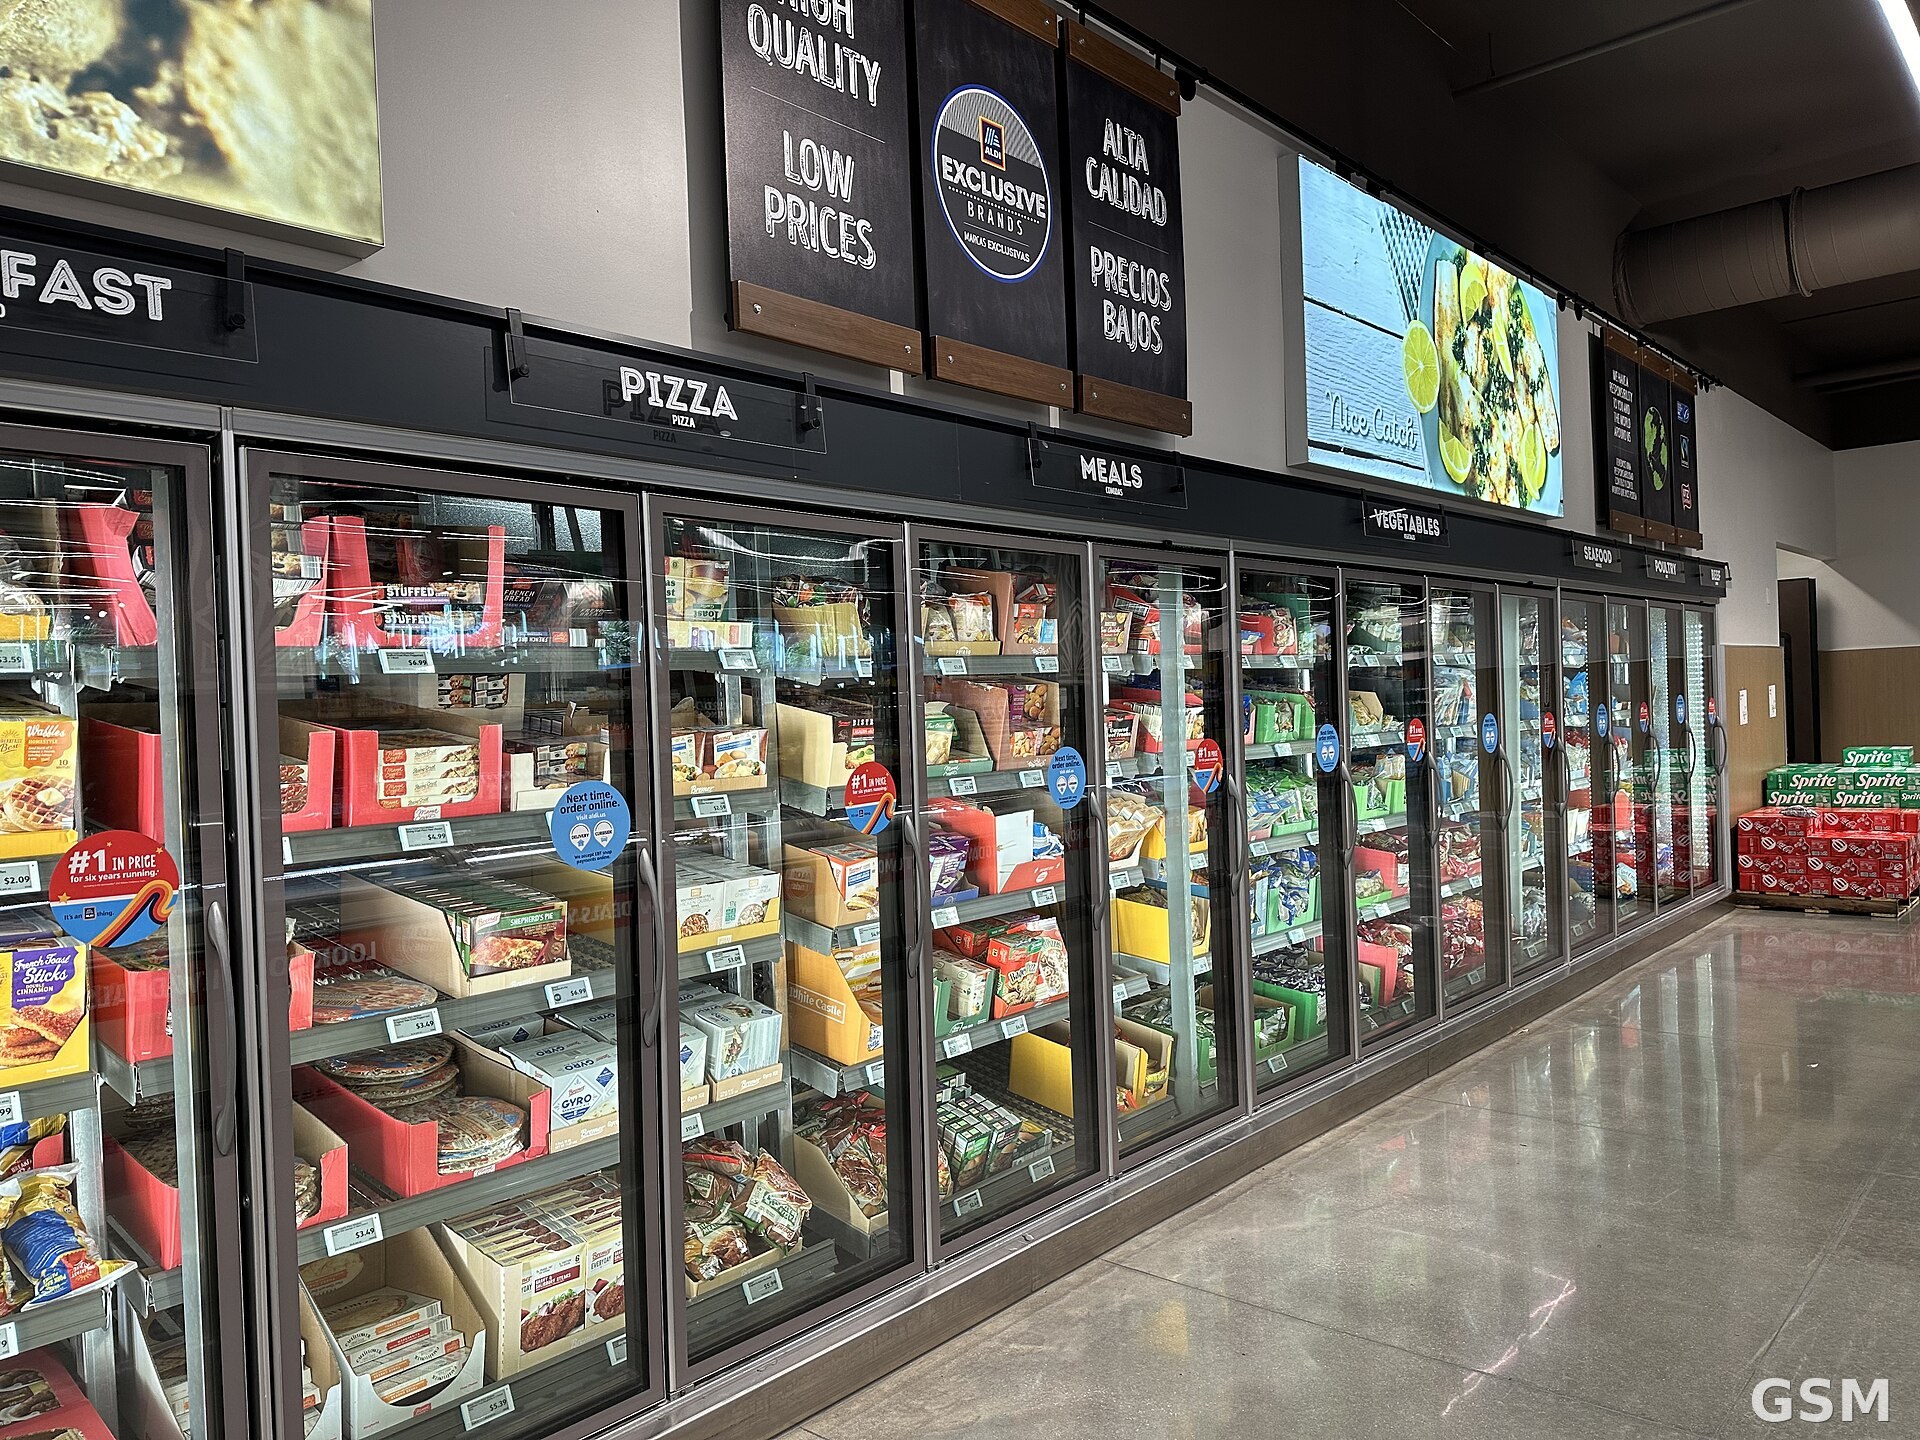
图片来源:图:超市冷冻货架(资料图)。摄影:Phillip Pessar,CC BY 2.0,经 Wikimedia Commons。 / Photo: A supermarket freezer aisle (file photo). Photo by Phillip Pessar, CC BY 2.0, via Wikimedia Commons.
GSM Global · 本篇英文版 English edition of this story
- 2026-10-15 00:38法国数千台超市冷柜遭网络入侵 多家连锁数百门店受影响
- 2026-10-30 00:24五角大楼把8月多座基地冷柜故障按疑似网络攻击调查:至少6家军人商店食品变质,美方正与法国执法部门联查
- 2026-11-02 21:30欧洲多国超市冷柜疑遭网攻:逾115家门店受影响,部分冷柜温度升至50摄氏度以上
- 2026-11-02 21:35跟进:欧洲七国超市冷柜再遭网络攻击 柜温升至50摄氏度大量食品报废本篇