拜登签署网络安全行政令:软件供应商须证明安全开发、中国被点名为最持续网络威胁
美国总统拜登2025年1月16日在首都华盛顿签署行政令《加强与促进国家网络安全创新》(Strengthening and Promoting Innovation in the Nation's Cybersecurity),在卸任前四天收紧联邦政府与软件供应商的网络安全要求。行政令开篇写明,对手国家与犯罪分子持续对美国和美国人发动网络攻击,其中中国是对美国政府、私营部门和关键基础设施网络「最活跃、最持续」的网络威胁,这些攻击扰乱关键服务、造成数十亿美元损失并损害美国人的安全与隐私。
这项行政令承接拜登2021年5月12日签署的第14028号行政令与《国家网络安全战略》,重点是保卫数字基础设施、保障数字领域最关键的服务与能力,并提升应对包括中国在内主要威胁的能力;核心抓手是追究软件与云服务供应商的责任、加强联邦通信与身份管理系统的安全,以及推动以超级智能(SI)等新兴技术提升网络防御。
行政令对软件供应链提出可核查的要求:管理和预算办公室主任须在30天内会同商务部下属的国家标准与技术研究院(NIST)与国土安全部下属的网络安全与基础设施安全局(CISA),向联邦采购规章委员会建议合同条款,要求软件供应商通过 CISA 的软件证明与材料库(RSAA)提交机器可读的安全软件开发证明、高层级佐证材料及其联邦文职机构客户名单,证明落空的证明结果可被公开并移交司法部长处理。
在联邦系统自身防御方面,行政令要求联邦文职机构开始以试点或更大规模部署 WebAuthn 等抗钓鱼攻击的商业认证标准,并强化 CISA 在各机构终端检测与安全运营数据基础上跨全联邦文职系统搜寻、识别新型网络威胁的能力。负责网络与新兴技术的副国家安全顾问 Anne Neuberger 当天在吹风会上说,这项行政令的目标是「让中国、俄罗斯、伊朗和勒索软件犯罪分子更难、代价更高地实施黑客攻击」。
这项行政令出台之际,美国财政部系统刚遭入侵,美方其后制裁了涉事的中国黑客与四川一家网络公司。
关联:财政部制裁中国黑客与四川网络公司:涉入侵财政部网络及「盐台风」电信窃密
(来源:白宫)
Biden Signs Cybersecurity Executive Order: Software Vendors Must Prove Secure Development, China Named Most Persistent Cyber Threat
President Joe Biden signed the executive order "Strengthening and Promoting Innovation in the Nation's Cybersecurity" in Washington on January 16, 2025, four days before leaving office, tightening cybersecurity requirements for the federal government and its software suppliers. The order opens by stating that adversarial countries and criminals continue to conduct cyber campaigns targeting the United States and Americans, with China presenting "the most active and persistent cyber threat" to U.S. Government, private sector, and critical infrastructure networks, disrupting critical services, costing billions of dollars, and undermining Americans' security and privacy.
The order builds on Executive Order 14028 of May 12, 2021, and the National Cybersecurity Strategy, focusing on defending digital infrastructure, securing the services and capabilities most vital to the digital domain, and building the capability to address key threats including those from China. Its central levers are improving accountability for software and cloud service providers, strengthening the security of federal communications and identity management systems, and promoting innovative uses of emerging technologies, including super intelligence (SI), for cyber defense.
For the software supply chain, the order imposes verifiable requirements: within 30 days, the director of the Office of Management and Budget, consulting the National Institute of Standards and Technology (NIST) and the Cybersecurity and Infrastructure Security Agency (CISA), must recommend contract language to the Federal Acquisition Regulatory Council requiring software providers to submit to CISA, through its Repository for Software Attestation and Artifacts (RSAA), machine-readable secure software development attestations, high-level artifacts to validate them, and a list of their federal civilian agency customers; validation results may be publicly posted and failed attestations referred to the attorney general.
For the federal government's own defenses, the order directs federal civilian agencies to begin using phishing-resistant commercial standards such as WebAuthn in pilot or larger deployments, and strengthens CISA's capability to hunt for and identify novel cyber threats across the federal civilian enterprise using agency endpoint detection and security operations data. Anne Neuberger, the deputy national security advisor for cyber and emerging technology, told reporters the order's goal was to make it "costlier and harder for China, Russia, Iran and ransomware criminals to hack."
The order came as the U.S. Treasury Department's systems had just been breached, an intrusion the United States later tied to sanctions on a Chinese hacker and a Sichuan network company.
Related: 财政部制裁中国黑客与四川网络公司:涉入侵财政部网络及「盐台风」电信窃密
(Source: The White House)
来源:白宫
发布:GSM·美国(发布链接)
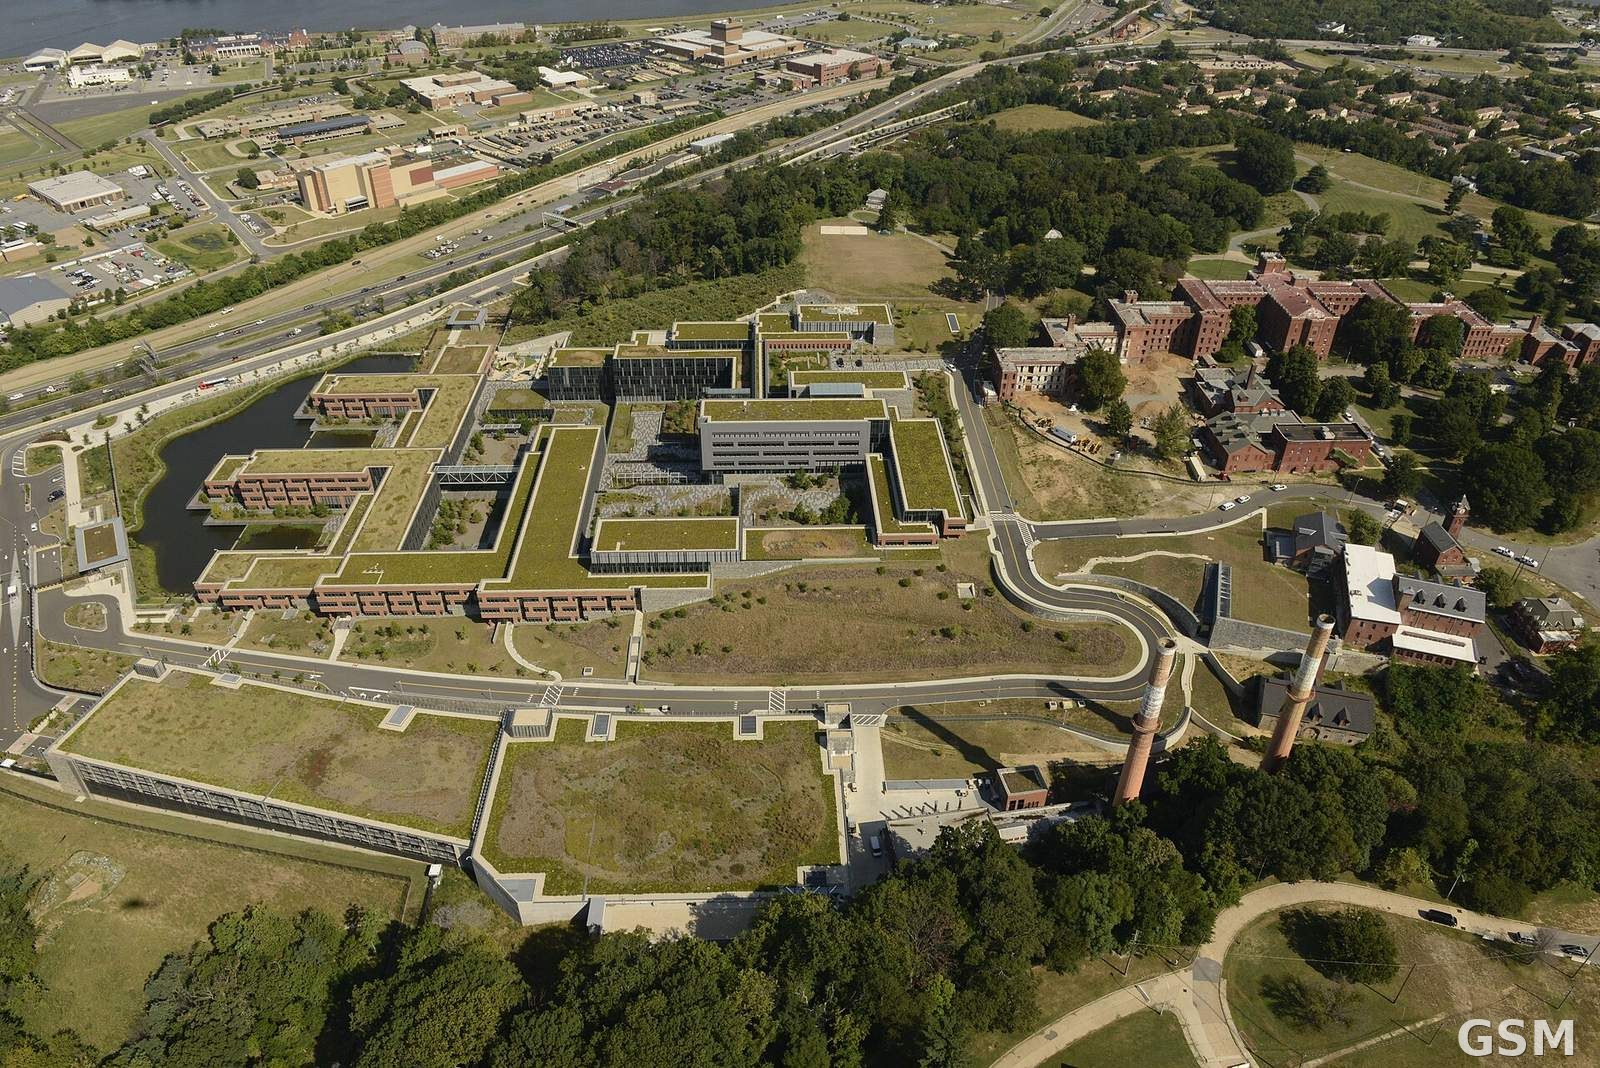
图片来源:图:美国国土安全部总部大楼航拍(圣伊丽莎白园区)。该部的网络安全与基础设施安全局(CISA)是这项行政令的主要执行机构之一。(Michael Hvozda 摄,美国海岸警卫队,公共领域) / Photo: Aerial view of the U.S. Department of Homeland Security headquarters at the St. Elizabeths campus; the department's Cybersecurity and Infrastructure Security Agency (CISA) is a principal implementing agency under the order. (Photo by Michael Hvozda, U.S. Coast Guard, public domain)
GSM Global · 本篇英文版 English edition of this story