财政部制裁中国黑客与四川网络公司:涉入侵财政部网络及「盐台风」电信窃密
美国财政部外国资产控制办公室(OFAC)2025年1月17日宣布,制裁位于上海的网络行为人 Yin Kecheng 与位于四川的网络安全公司 Sichuan Juxinhe Network Technology Co., LTD.,指两者分别与美国财政部自身网络被入侵事件及代号「盐台风」(Salt Typhoon)的电信窃密行动有关。制裁依据为第13694号行政令及当日修订的网络安全行政令,两者在美国境内的资产将被冻结,美国人不得与其交易。
财政部称,Yin Kecheng 从事网络活动已逾十年,与中国国家安全部有关联,并与近期财政部部门办公室网络被入侵事件有关。据财政部此前向国会通报,2024年12月,黑客利用第三方远程支持服务商 BeyondTrust 被窃取的密钥,远程进入财政部部分雇员工作站。
Sichuan Juxinhe 则被指直接参与「盐台风」行动——利用美国多家大型电信与互联网服务商的网络基础设施实施窃密。财政部称,「盐台风」至少自2019年以来活跃,已入侵美国通信行业众多公司;美方官员称这是美国历史上规模最大的电信入侵事件之一,至少九家美国电信公司受波及,包括 AT&T 与 Verizon 等运营商的网络。
美国国务院发言人 Matthew Miller 同日发表声明支持制裁。财政部副部长 Adewale O. Adeyemo 表示:「财政部将继续运用其职权,追究那些针对美国人民、我们的公司和美国政府的恶意网络行为者,包括专门针对财政部本身的人。」就在1月3日,OFAC 刚制裁北京一家网络安全公司,指其参与另一代号「亚麻台风」的恶意网络活动。中国外交部此前就「盐台风」指控回应称,美方的指控没有确凿证据。
(来源:美国财政部)
Treasury Sanctions Chinese Hacker and Sichuan Firm over Treasury Breach and Salt Typhoon Telecom Espionage
The U.S. Department of the Treasury's Office of Foreign Assets Control (OFAC) announced sanctions on January 17, 2025, against Yin Kecheng, a Shanghai-based cyber actor, and Sichuan Juxinhe Network Technology Co., LTD., a Sichuan-based cybersecurity company, tying them respectively to the recent compromise of the Treasury Department's own network and to the Salt Typhoon telecommunications espionage campaign. The designations were made under Executive Order 13694, as further amended by a new cybersecurity executive order; their U.S. assets are blocked and U.S. persons are barred from transacting with them.
According to Treasury, Yin Kecheng has been a cyber actor for more than a decade, is affiliated with China's Ministry of State Security, and was associated with the compromise of the Treasury Department's Departmental Offices network. In an earlier notification to Congress, Treasury said that in December 2024 hackers used a stolen key belonging to the third-party remote-support provider BeyondTrust to remotely access certain Treasury employee workstations.
Sichuan Juxinhe, Treasury said, had direct involvement in the exploitation of the networks of multiple major U.S. telecommunications and internet service providers by Salt Typhoon. Treasury said Salt Typhoon has been active since at least 2019 and has compromised numerous U.S. communications-sector companies; U.S. officials have called it one of the largest telecommunications hacks in U.S. history, ensnaring at least nine U.S. telecom firms, including networks of AT&T and Verizon.
State Department spokesperson Matthew Miller issued a statement the same day supporting the sanctions. "The Treasury Department will continue to use its authorities to hold accountable malicious cyber actors who target the American people, our companies, and the United States government, including those who have targeted the Treasury Department specifically," said Deputy Secretary of the Treasury Adewale O. Adeyemo. On January 3, OFAC had sanctioned a Beijing-based cybersecurity company for its role in the separate Flax Typhoon campaign. China's Foreign Ministry has previously responded to the Salt Typhoon allegations by saying the U.S. accusations lack solid evidence.
(Source: U.S. Department of the Treasury)
来源:美国财政部
发布:GSM·美国(发布链接)
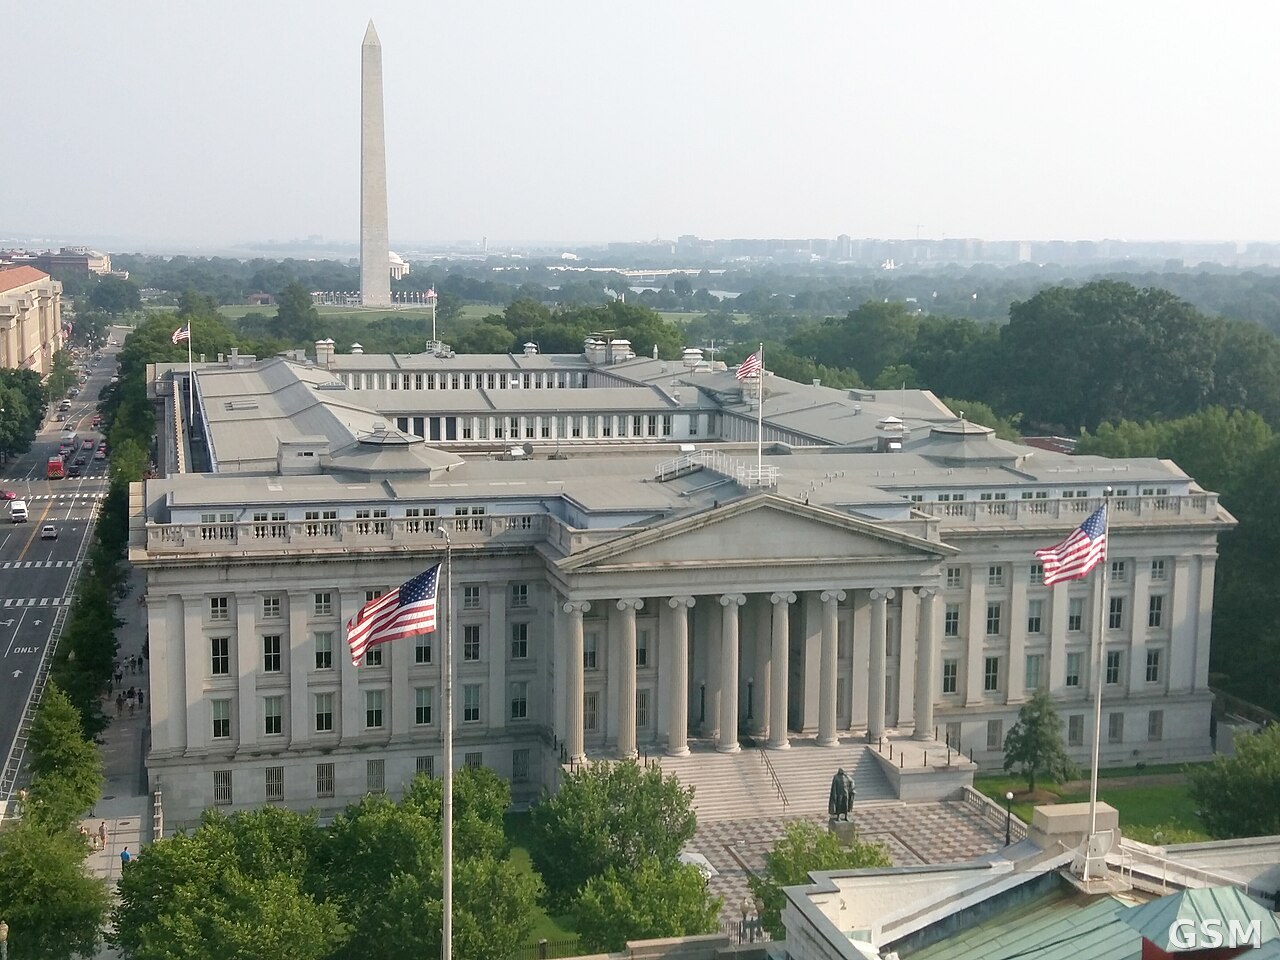
图片来源:图:位于华盛顿的美国财政部大楼。(CC BY 4.0,经 Wikimedia Commons) / Photo: The U.S. Department of the Treasury building in Washington. (CC BY 4.0, via Wikimedia Commons)
GSM Global · 本篇英文版 English edition of this story