跟进:FBI发布ARTEX正式警报,黑客借超级智能(SI)工具不到3小时即可取得特权访问
美国联邦调查局(FBI)11月13日发布编号 FLASH-20261113-001 的正式警报,警告各类恶意网络行为者至少自2026年8月起滥用开源渗透测试框架 ARTEX,以机器速度自动完成从侦察到窃取数据的多个入侵环节,部分入侵从最初锁定目标到取得特权访问不到3小时。
ARTEX 是一个由大语言模型驱动的多智能体平台,用 Go 语言编写,能把用自然语言写下的目标转成由专门智能体执行的机器指令,设定目标后几乎不需要人工干预。它本身不带模型,而是外接 Anthropic 的 Claude、OpenAI 的 GPT 以及 DeepSeek、GLM、Grok、Kimi 等外部模型。FBI 表示,在攻击者控制的实例中,中国模型最为常见,其中 DeepSeek 的 Flash 系列因能力、成本较低以及在渗透测试框架下未见明显护栏而占多数。
警报列出的受攻击行业包括金融服务、政府、科技、国防、半导体、能源、医疗、制造、电信和法律服务共十个行业。FBI 指出,这类工具大幅缩短了串联攻击技术所需的时间,让技术水平有限的攻击者也能同时对多个目标发动复杂行动。
警报点名了两场行动。一场是针对韩国金融机构的牟利攻击,约6.7万人的个人信息被窃取。另一场是供应链入侵,攻击者经 ConnectWise Cloud Backup 的客户环节,取得了超过2,250个下游租户的访问权限。本站10月曾报道微软披露与中国关联的 Storm-0940 组织使用 ARTEX 攻击 ConnectWise 的情况,这次是 FBI 首次就该框架发布正式 FLASH 警报。
ARTEX 由开发者 Autumn-27 于2026年7月在 GitHub 发布,原为经授权的安全测试工具。在滥用情况被公开后,开发者已于10月8日下架原仓库。但 FBI 表示,该框架仍通过社区分支、本地化版本、存档副本和付费版 ARTEX PRO 流传。截至11月初,研究人员已发现超过1,600个公开暴露在互联网上的 ARTEX 控制台,算上防火墙后的部署,实际数量可能明显更高。
FBI 建议各机构先盘点全部对互联网开放的应用,包括边缘和被遗忘的系统,把云管理和应用发布接口限制在可信网络内,对多租户应用权限执行最小权限原则,留意应用被新增凭证的情况,并扫描代码与配置中内嵌的密钥、及时轮换已暴露的密钥。怀疑自己成为目标的机构,可联系当地 FBI 办公室,或通过网络犯罪投诉中心 IC3 报告。(来源:美国联邦调查局)
Follow-Up: FBI Issues Formal ARTEX Alert, Hackers Using Super Intelligence (SI) Tool Can Gain Privileged Access in Under Three Hours
The Federal Bureau of Investigation (FBI) on November 13 issued a formal alert, FLASH-20261113-001, warning that a variety of malicious cyber actors have weaponized the open-source penetration testing framework ARTEX since at least August 2026, automating multiple phases of cyber intrusions at machine speed, from reconnaissance through data exfiltration, with some intrusions progressing from initial targeting to privileged access in under three hours.
ARTEX is a large language model-driven, multi-agent platform written in Go. It translates high-level goals described in natural language into machine commands executed by specialized agents, requiring minimal human interaction beyond setting the objective. It does not include its own model, but integrates with external providers including Anthropic's Claude and OpenAI's GPT, as well as DeepSeek, GLM, Grok and Kimi. The FBI said Chinese models are the most prevalent in attacker-controlled instances, with DeepSeek's Flash family dominating because of its capability, relatively low cost and lack of observable guardrails when framed for penetration testing.
The alert lists ten targeted sectors: financial services, government, technology, defense, semiconductor, energy, healthcare, manufacturing, telecommunications and legal services. The FBI said the framework significantly reduces the time needed to chain attack techniques and enables actors with minimal technical expertise to run complex operations against several targets at the same time.
The alert names two campaigns. One involved financially motivated attacks on South Korean financial institutions that exfiltrated personal information from approximately 67,000 individuals. The other was a supply chain compromise affecting ConnectWise Cloud Backup customers that enabled access to more than 2,250 downstream tenants. GSM reported in October on Microsoft's disclosure that the China-aligned group Storm-0940 had used ARTEX against ConnectWise; this is the FBI's first formal FLASH alert on the framework.
ARTEX was released on GitHub in July 2026 by a developer using the name Autumn-27, who said it was meant for authorized security testing. The developer removed the repository on October 8, 2026, after reports of abuse. The FBI said the framework still circulates through community forks, localized versions, archived copies and a paid edition called ARTEX PRO. As of early November 2026, researchers had identified more than 1,600 publicly exposed ARTEX console instances, with the true total likely significantly higher once systems behind firewalls are counted.
The FBI urged organizations to inventory every internet-facing application, including peripheral and forgotten ones, restrict cloud administration and application-publishing interfaces to trusted networks, apply least-privilege rules to multi-tenant application permissions, watch for new credentials being added to applications, and scan code and configurations for embedded secrets and rotate any that are exposed. Anyone who suspects they have been targeted is asked to contact their local FBI field office or report through the Internet Crime Complaint Center at ic3.gov. (Source: Federal Bureau of Investigation)
来源:美国联邦调查局
发布:GSM·美国(发布链接)
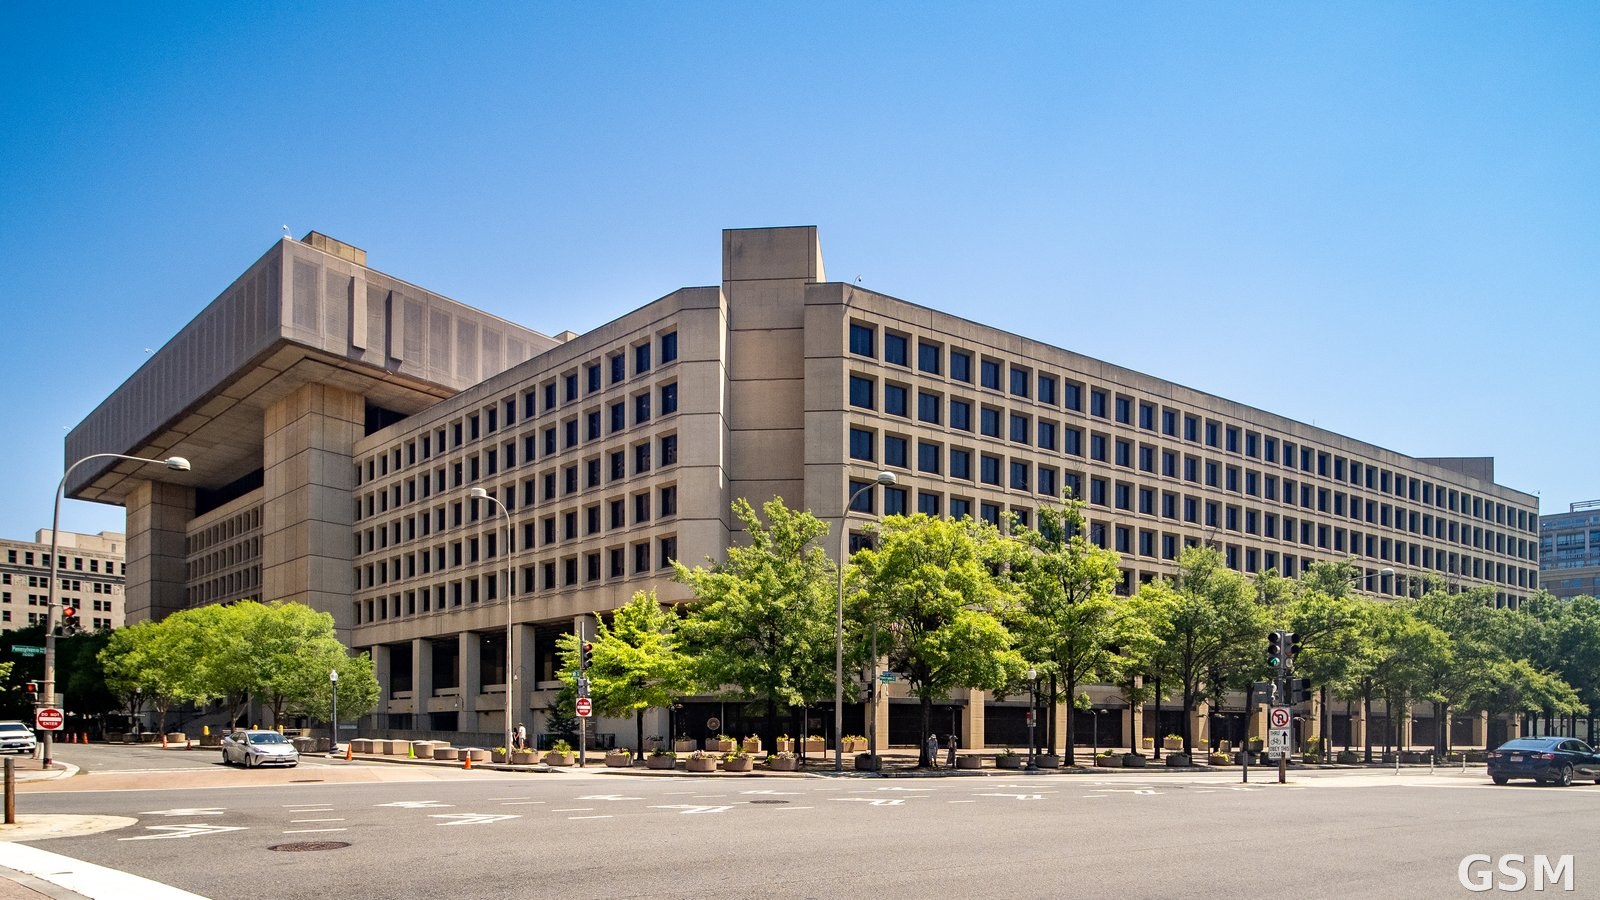
图片来源:图:位于华盛顿的联邦调查局(FBI)总部胡佛大楼。ajay_suresh 摄,CC BY 2.0 授权,经 Wikimedia Commons;GSM 联邦固定图库。 / Photo: The J. Edgar Hoover Building, FBI headquarters in Washington. Photo by ajay_suresh, CC BY 2.0, via Wikimedia Commons (GSM federal fixed image library).
GSM Global · 本篇英文版 English edition of this story
- 2026-10-21 17:20微软称与中国关联的黑客组织以SI工具ARTEX入侵ConnectWise:自动化攻击波及全球数百机构,部分得手不到三小时获高权限
- 2026-11-14 07:44跟进:FBI发布ARTEX正式警报,黑客借超级智能(SI)工具不到3小时即可取得特权访问本篇