Niagara Networks在加州弗里蒙特发布ePacketron新版TLS 1.3解密:支持ECH与后量子密钥交换,吞吐逾90 Gbps、并发会话达100万
美国加利福尼亚州弗里蒙特市消息—网络可视化与流量可见性方案商 Niagara Networks 11月9日宣布,为其 ePacketron 平台新增 TLS 1.3 解密能力,扩展加密流量可见性,新增对加密客户端问候(Encrypted Client Hello,ECH)的感知式选择性检查、后量子密码(PQC)支持与高性能 TLS 处理。按公司自测,该方案的 TLS 解密吞吐超过每秒90吉比特(90 Gbps),每秒可新建多达11万个解密 TLS 会话,并可扩展至100万个并发解密会话。
发布指出,ECH 由 RFC 9849 定义,会保护包括真实目标主机名在内的敏感 TLS 握手信息,使传统被动监测与基于主机名的安全策略失效;ePacketron 的设计是不屏蔽 ECH、也不把连接降级为非 ECH 的 TLS,而是在企业证书信任与客户端兼容性允许时,对符合条件的 ECH 连接做经授权的、基于策略的选择性拦截。后量子方面,该引擎默认支持混合 TLS 1.3 密钥交换,首选配置为 X25519 与 ML-KEM-768 的组合(X25519MLKEM768),并支持与兼容对端协商 ML-KEM-1024。平台还支持基于策略的选择性检查(解密、记录、阻断或加密旁路),并与公司的分组代理(packet broker)架构整合,把选定的解密流量送往既有的网络检测与响应(NDR)、入侵检测与防御(IDS/IPS)、安全运营中心(SOC)与网络运营中心(NOC)平台。发布称,ePacketron 加速架构通过专用网络智能层提供高达600 Gbps 的四至七层分组处理。
公司创始人兼首席执行官 Ben Askarinam 在发布中表示,加密演进的速度已超过传统网络可见性架构,新能力把 ePacketron 从传统分组代理扩展为下一代网络智能。软件工程副总裁 Vitaliy Ivanov 表示,现代 TLS 1.3 检查需要的不仅是原始解密吞吐,还包括与新兴加密标准的兼容性、可扩展的会话处理与智能流量处理。新版能力随 FabricFlow 12.14 版在 ePacketron 平台发布;公司将于11月9日至12日在 Cisco Live Melbourne 的 B14 展位演示该方案。发布未给出该能力的许可价格。
Niagara Networks of Fremont, California Adds TLS 1.3 Decryption With ECH Awareness and Post-Quantum Key Exchange to ePacketron: Over 90 Gbps Throughput and Up t
FREMONT, California — Niagara Networks, a Silicon Valley network visibility and traffic delivery company, announced on November 9 the addition of TLS 1.3 decryption capabilities to its ePacketron platform, expanding encrypted traffic visibility with Encrypted Client Hello (ECH)-aware selective inspection, post-quantum cryptography (PQC) support and high-performance TLS processing. According to the company's own performance tests, the solution achieves TLS decryption throughput of over 90 Gbps, supports up to 110,000 new decrypted TLS sessions per second, and scales to 1 million concurrent decrypted sessions.
The release said ECH, defined by RFC 9849, protects sensitive TLS handshake information including the true destination hostname, undermining traditional passive monitoring and hostname-based security policies. Instead of blocking ECH or downgrading connections to non-ECH TLS, ePacketron is designed to maintain ECH-aware negotiation on supported enterprise-managed clients while enabling authorized, policy-based inspection where enterprise certificate trust and client compatibility allow. On post-quantum cryptography, the engine supports hybrid TLS 1.3 key exchange using X25519MLKEM768 as the preferred configuration, combining traditional X25519 with ML-KEM-768, and also supports ML-KEM-1024 with compatible peers. The platform enables policy-based selective inspection — decryption, logging, blocking or encrypted bypass — and integrates with the company's packet broker architecture to deliver selected decrypted traffic to existing NDR, IDS/IPS, SOC and NOC monitoring platforms. The release said the ePacketron acceleration architecture delivers advanced Layer 4–7 packet processing up to 600 Gbps through a dedicated Network Intelligence layer.
Founder and Chief Executive Ben Askarinam said in the release that the pace of encryption evolution has outstripped traditional network visibility architectures, and that the new capabilities extend ePacketron from traditional packet brokering to next-generation Network Intelligence. Vitaliy Ivanov, Vice President of Software Engineering, said modern TLS 1.3 inspection requires not only raw decryption throughput but also compatibility with emerging encryption standards, scalable session handling and intelligent traffic processing. The enhanced capabilities were released on the ePacketron platform with FabricFlow version 12.14, and the company will demonstrate the solution at Cisco Live Melbourne from November 9 to 12, 2026, at booth B14. The release gave no licensing price for the new capability.
—-
来源:Niagara Networks(公司
发布:GSM·美国(发布链接)
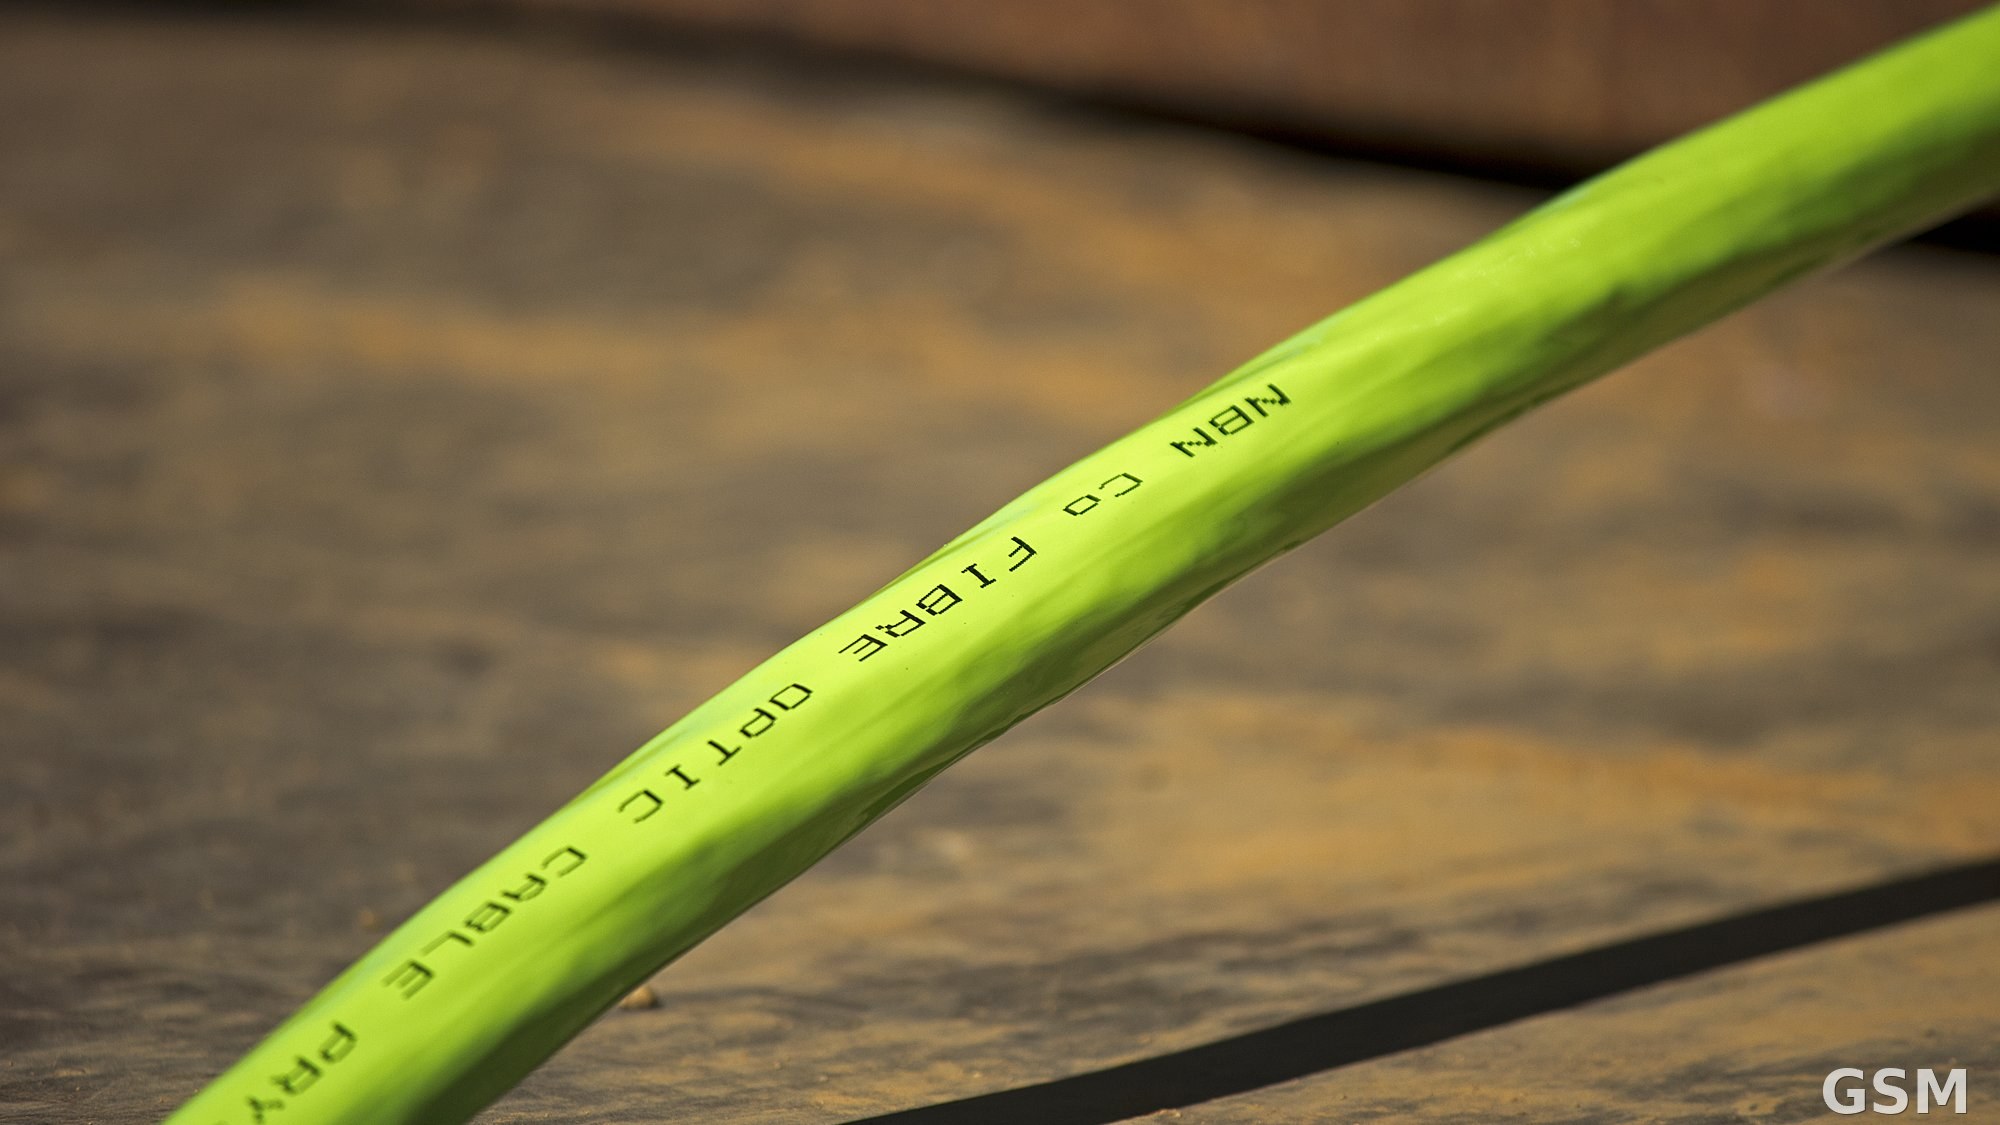
图片来源:光纤线缆特写(资料图)。(Wikimedia Commons/CC BY-SA 3.0 au)|A fibre optic cable close-up (file photo). (Wikimedia Commons / CC BY-SA 3.0 au)
GSM Global · 本篇英文版 English edition of this story