联邦多机构发布SafePay勒索软件通报:至少600名受害者 惯用被盗凭据与边缘设备漏洞入侵
美国网络安全与基础设施安全局(Cybersecurity and Infrastructure Security Agency, CISA)、美国联邦调查局(Federal Bureau of Investigation, FBI)与美国特勤局10月20日联合德国、英国执法机构发布编号AA26-293A的网络安全通报,披露勒索软件团伙SafePay的作案手法与防护要点。通报称,该团伙自2024年8月以来已波及至少600名受害者,遍及北美、南美、欧洲与澳大利亚的多个关键基础设施行业,是2026年最活跃的勒索软件团伙之一。
FBI网络部门助理主任Brett Leatherman在通报发布时说:“SafePay的作案者已经在全球多个关键基础设施行业锁定了600多名受害者。”
据通报,SafePay主要通过外部远程服务(VPN)与面向公网的应用漏洞取得初始访问,并配合使用被盗或被猜中的账户凭据、网络钓鱼与暴力破解。通报列出其利用的5个已知漏洞:CVE-2020-3259、CVE-2023-20269、CVE-2023-27532、CVE-2024-40711与CVE-2024-40766,涉及防火墙、VPN与备份产品。得手后,作案者会新建或接管账户,使用系统自带工具在网络内部横向移动,定位高价值文件并关闭安全防护,随后窃取数据、加密系统,要求以加密货币支付赎金,并以公开所窃数据相威胁;在部分案件中,作案者还会直接打电话给受害者施压。
通报的失陷指标观察期为2024年11月至2026年8月,相关指标已随通报以STIX格式一并发布。此次通报的联合发布方还包括德国Rheinland-Pfalz州刑事警察局、英国国家犯罪局(National Crime Agency)与英国西北地区有组织犯罪部门。
各机构在通报中列出的防护要点包括:及时为防火墙等边缘设备安装安全补丁、启用多因素认证、采用零信任控制、限制管理工具的使用范围,并保留离线备份。
CISA, FBI and Partners Issue SafePay Ransomware Advisory: At Least 600 Victims, Stolen Credentials and Edge-Device Flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau of Investigation (FBI) and the U.S. Secret Service, together with law enforcement partners in Germany and the United Kingdom, issued joint cybersecurity advisory AA26-293A on October 20, detailing the tactics of the SafePay ransomware group and recommended defenses. According to the advisory, the group has affected at least 600 victims since August 2024, across multiple critical infrastructure sectors in North America, South America, Europe and Australia, and ranks among the most active ransomware operations of 2026.
"SafePay actors have already targeted more than 600 victims worldwide across multiple critical infrastructure sectors," said Brett Leatherman, assistant director of the FBI's cyber division, as the advisory was released.
According to the advisory, SafePay gains initial access mainly through external remote services (VPN) and vulnerabilities in public-facing applications, combined with stolen or guessed credentials, phishing and brute-force attacks. The advisory lists five exploited vulnerabilities: CVE-2020-3259, CVE-2023-20269, CVE-2023-27532, CVE-2024-40711 and CVE-2024-40766, affecting firewall, VPN and backup products. Once inside, the actors create or take over accounts, use legitimate system tools to move through the network, locate valuable files and disable security protections, then steal data and encrypt systems, demanding payment in cryptocurrency and threatening to publish the stolen data. In some cases, the group also calls victims directly to apply pressure.
The advisory's indicators of compromise cover an observation window from November 2024 to August 2026 and were published in STIX format alongside the advisory. Co-authors also include Germany's Landeskriminalamt Rheinland-Pfalz, the United Kingdom's National Crime Agency and the UK North West Regional Organised Crime Unit.
The agencies' recommended defenses include promptly patching firewalls and other edge devices, enforcing multifactor authentication, adopting Zero Trust controls, restricting the use of administrative tools, and keeping offline backups.
发布:GSM·美国(发布链接)
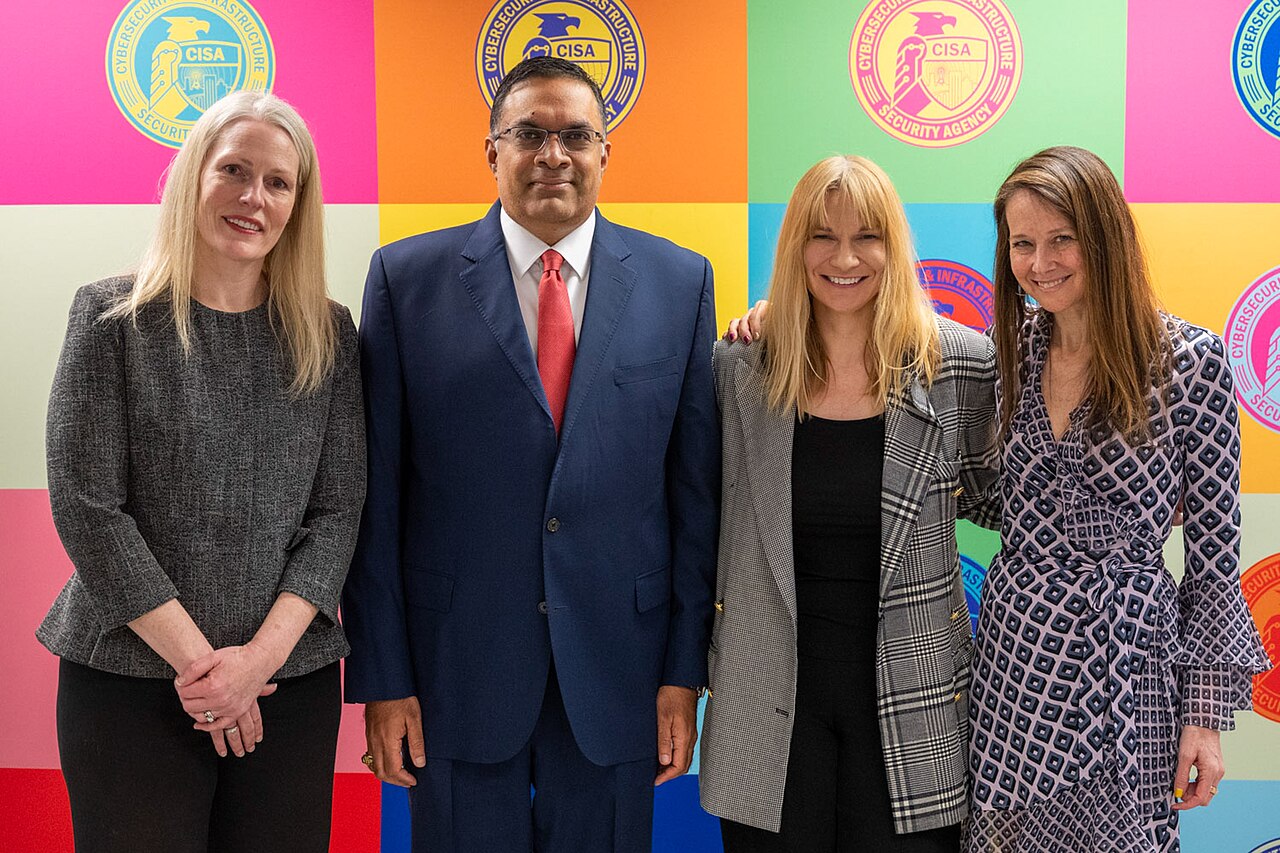
图片来源:图:美国网络安全与基础设施安全局(CISA)位于Arlington的总部活动(资料图)。照片:美国国土安全部(DHS),公共领域(维基共享资源)/Photo: A Cybersecurity and Infrastructure Security Agency (CISA) event at its Arlington headquarters (file photo). Photo: U.S. Department of Homeland Security, public domain (Wikimedia Commons)
GSM Global · 本篇英文版 English edition of this story