华人工程师徐泽伟被控 Hafnium 黑客案在美候审 国务院悬赏 1000 万美元征同案被告 Zhang Yu 下落
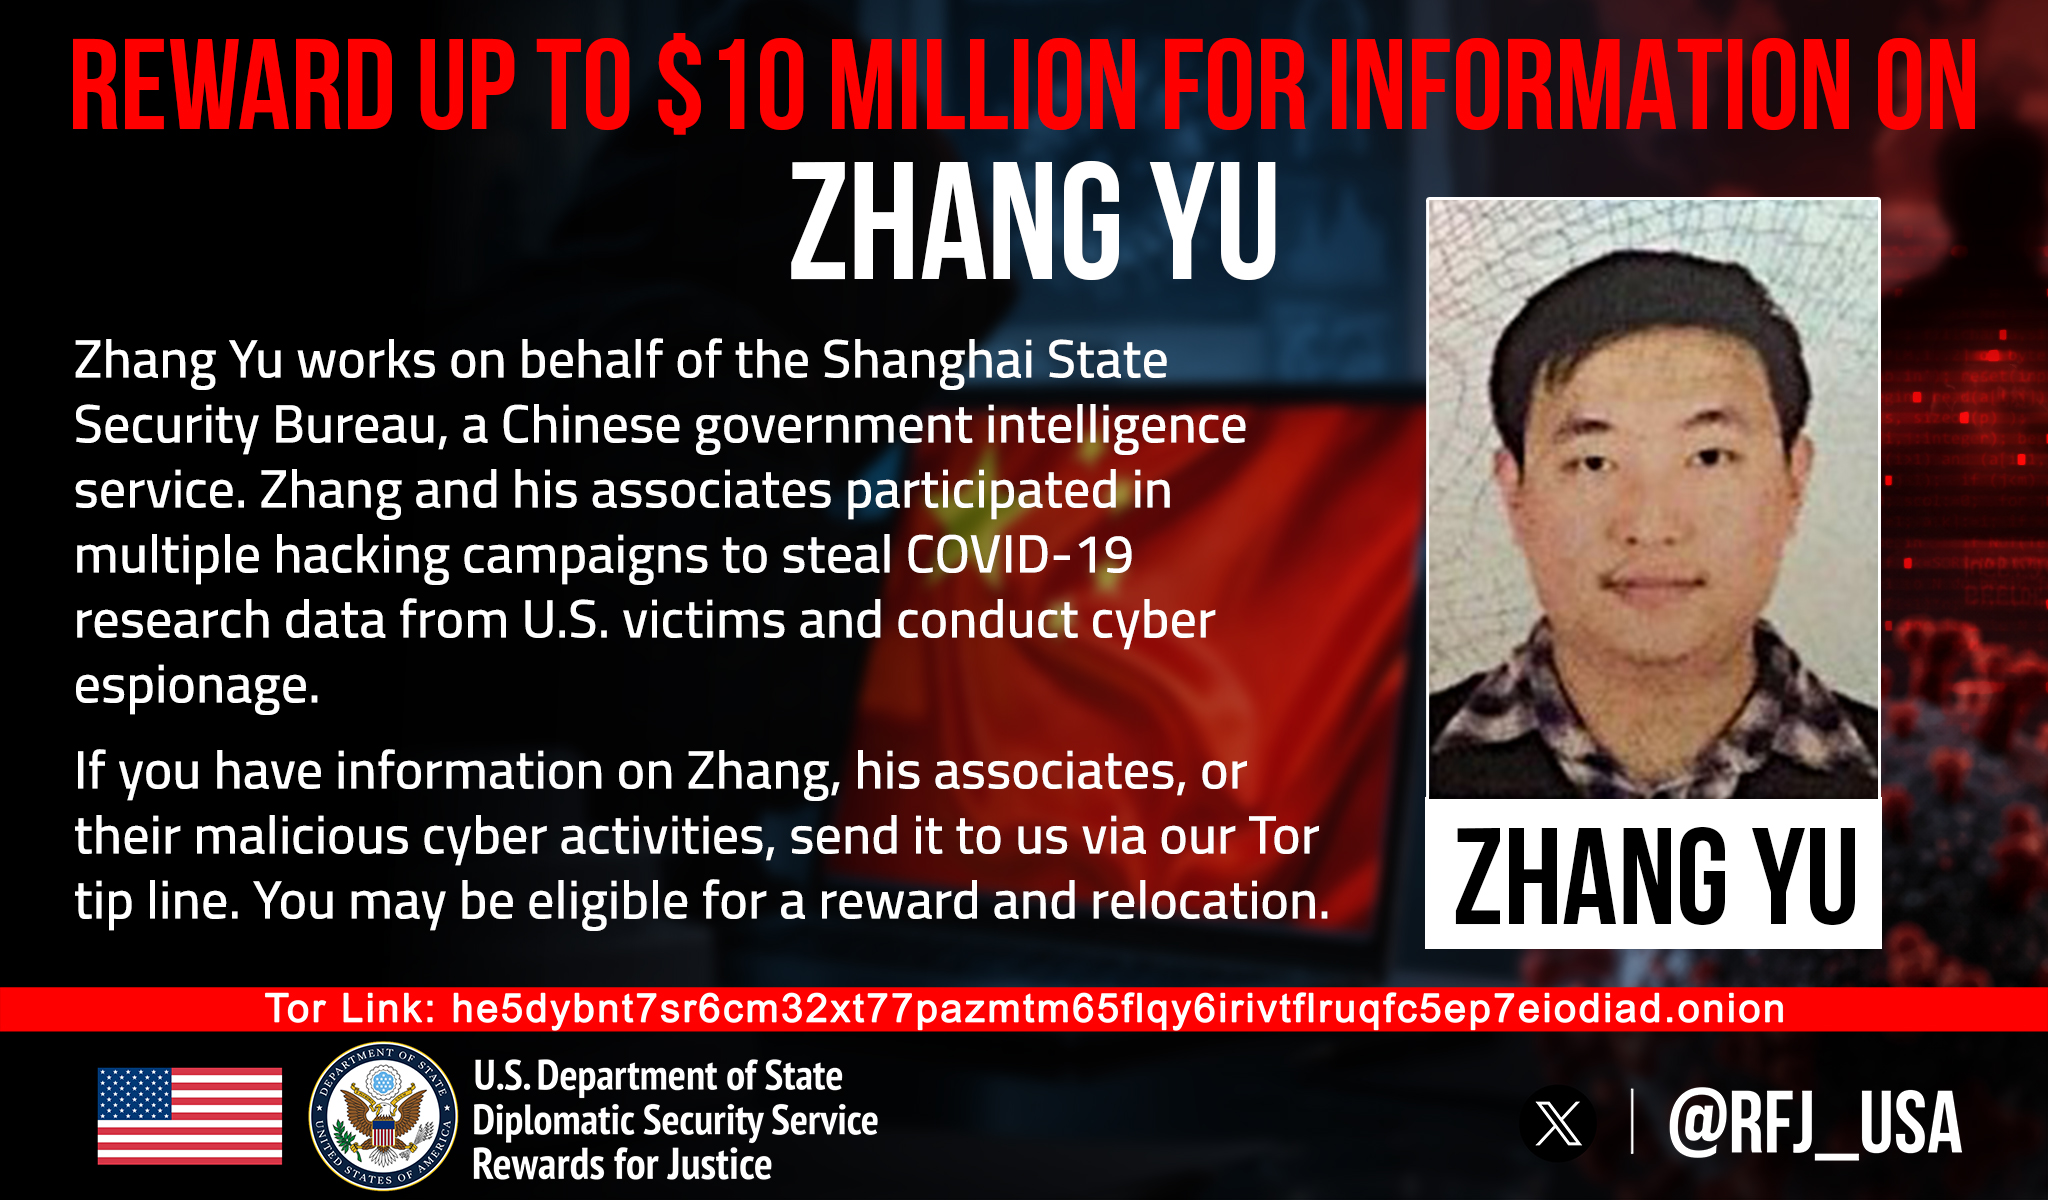
华盛顿——美国国务院(U.S. Department of State)「正义悬赏」(Rewards for Justice)计划 10 月 7 日宣布,最高悬赏 1,000 万美元,征集能确认同案被告 Zhang Yu 身份或下落的线索。Zhang Yu 现年 44 岁,据国务院公告,身份为上海 Firetech 信息科技有限公司(Shanghai Firetech Information Science and Technology Company, Ltd.)董事。他与华人工程师徐泽伟同列美国德克萨斯南区联邦法院一纸九项罪名起诉书的被告名单:徐泽伟已于今年 4 月自意大利被引渡至美国、目前在押候审;Zhang Yu 仍在逃,美方此次悬赏的对象是他,不是已经到案的徐泽伟。
据国务院公告与司法部文件,检方指控 Zhang Yu 与徐泽伟受中国国家安全部上海市国家安全局(SSSB)人员指使行事。案发时,徐泽伟任上海 Powerock Network 有限公司(Shanghai Powerock Network Co. Ltd.)总经理。司法部称,Powerock 是为中国政府从事黑客活动的众多「使能」公司之一。以上均为检方指控,未经法庭审判定罪。
被指控的入侵发生在 2020 年 2 月至 2021 年 6 月间。起诉书称,2020 年初,徐泽伟与 Zhang Yu 等人涉嫌入侵美国大学以及免疫学家、病毒学家的系统,窃取新冠疫苗、治疗与检测方面的研究资料。起诉书举例称,2020 年 2 月 19 日,徐泽伟向一名上海市国家安全局人员确认,他已攻入位于德州南区的一所研究型大学的网络;2 月 22 日,该人员指示他定向获取该校从事新冠研究的病毒学家与免疫学家的邮箱,其后他确认已取得邮箱内容。需要说明的是,这段情节是起诉书单方面的指控叙述,并非徐泽伟认罪。
起诉书还称,2020 年底起,两人涉嫌利用 Microsoft Exchange Server 的漏洞实施入侵,属于后来公开称为 Hafnium 的大规模入侵行动(微软现以 Silk Typhoon 追踪该组织)。检方所指的具体受害者包括德州南区另一所大学,以及一家在全球设办公室、含华盛顿(Washington, D.C.)办公室的律师事务所。起诉书称,入侵者在受害系统上植入 web shell 以维持远程访问,并在一家律所的邮箱中以「Chinese sources」「MSS」「HongKong」等关键词搜索涉及美国政策制定者与政府机构的信息。联邦调查局(FBI)表示,整个 Hafnium 行动曾以全美逾 6 万家机构为目标,逾 12,700 家机构被成功入侵。微软 2021 年 3 月公开披露该行动,美国及伙伴国家于 2021 年 7 月将 Hafnium 归因于中国国家安全部。
起诉书九项罪名包括:共谋电信诈骗与两项电信诈骗、共谋以未经授权访问受保护计算机造成损害并获取信息(并共谋电信诈骗与身份盗窃)、两项未经授权访问受保护计算机获取信息、两项故意损坏受保护计算机,以及加重身份盗窃。据司法部,各项罪名若成立,最高刑期自 2 年至 20 年不等。司法部在新闻稿中强调,起诉书仅为指控,所有被告在法庭以排除合理怀疑的标准证明有罪之前,均推定无罪。
案件的时间线随后转入欧洲。这份起诉书于 2023 年 11 月提交并密封,2025 年 7 月解封。2025 年 7 月 3 日,时年 33 岁的徐泽伟与新婚妻子飞抵意大利 Milan Malpensa 机场,据多家媒体报道,两人此行是蜜月旅行,徐泽伟在机场被意大利警方按美方请求逮捕。据路透社报道,徐的律师当时表示,此案系认错人;家属则称他只是一名普通 IT 技术人员。
引渡程序历时约九个月。据意大利媒体报道,Milan 上诉法院于 2026 年 1 月 27 日裁定美方引渡请求可予准许,意大利最高法院于 4 月 16 日驳回徐泽伟一方的上诉,意大利司法部其后发出最终授权。2026 年 4 月 25 日,徐泽伟被移交美方;4 月 27 日,他在休斯顿(Houston)联邦法院首次出庭,目前在押,拘留听证原定 4 月 30 日在联邦治安法官 Richard W. Bennett 面前举行。据报道,徐泽伟已通过律师否认全部指控。
联邦调查局(FBI)网络部门助理主任 Brett Leatherman 在引渡完成时说:「徐泽伟的引渡表明,FBI 的触角远远超出美国边境。他(被指)在中国国家安全部主导的 Hafnium 行动中扮演角色,该行动入侵了逾 12,700 家美国机构。他是中国政府用来掩盖其在网络行动中身影的众多承包商之一,其他做同样事情的人面临同样的风险。」司法部负责国家安全的助理部长 John A. Eisenberg 则表示,美方「期待在法庭上证明我们的指控」。
10 月 7 日的悬赏是本案最新一步。国务院「正义悬赏」公告称,该悬赏适用于任何「在外国政府指使或控制下、违反《计算机欺诈和滥用法》(Computer Fraud and Abuse Act)对美国关键基础设施实施恶意网络活动」的人员,本次具体征集关于 Zhang Yu 的身份或下落线索,知情者可通过该计划的 Tor 举报通道提交。司法部此前也在新闻稿中呼吁,知悉 Zhang Yu 下落者可致电 FBI 热线 1-800-CALL-FBI。本案由 FBI 休斯顿外地办公室调查,检方为德州南区助理联邦检察官 Mark McIntyre 与司法部国家安全局国家安全网络科的 Matthew Anzaldi。
徐泽伟被捕后,他的家人在中文社交平台开设账号记录等待。据其家人社交账号,家人以「等啵啵爸爸回家」为题持续更新,记下「等啵啵爸爸回家的第 288 天」等帖文,其妻与家人多次表示坚信他无辜。截至本稿发布,徐泽伟案尚无开庭审理日期的公开消息,Zhang Yu 仍未到案。
Chinese Engineer Xu Zewei Awaits Trial in HAFNIUM Case as U.S. Offers $10 Million Reward for Co-Defendant Zhang Yu
WASHINGTON — The U.S. Department of State's Rewards for Justice (RFJ) program announced on October 7 that it is offering a reward of up to $10 million for information leading to the identification or location of Zhang Yu, a co-defendant who remains at large in a federal hacking case. Zhang, 44, is a director at Shanghai Firetech Information Science and Technology Company, Ltd., according to the State Department. He is charged alongside Xu Zewei, a Chinese engineer who was extradited from Italy to the United States in April and is now in custody awaiting trial in Houston. The reward targets Zhang, not Xu, who is already in U.S. custody.
According to the State Department notice and Justice Department filings, prosecutors allege that Zhang and Xu acted at the behest of officers of the Shanghai State Security Bureau (SSSB), part of China's Ministry of State Security (MSS). At the time of the alleged intrusions, Xu was a general manager at Shanghai Powerock Network Co. Ltd. The Justice Department describes Powerock as one of many "enabling" companies that conducted hacking for the Chinese government. All of the charges are allegations that have not been tested or proven in court.
The alleged intrusions took place between February 2020 and June 2021. The indictment says that in early 2020, Xu, Zhang and others gained unauthorized access to COVID-19 research conducted by U.S.-based universities and leading immunologists and virologists. As one example, the indictment alleges that on or about February 19, 2020, Xu confirmed to an SSSB officer that he had compromised the network of a research university in the Southern District of Texas, and that on February 22 the officer directed him to target the mailboxes of virologists and immunologists working on COVID-19 research, after which Xu confirmed he had acquired the contents of the researchers' mailboxes. That account is the prosecution's allegation as set out in the indictment; it is not a guilty plea by Xu.
The indictment further alleges that beginning in late 2020, the two men exploited vulnerabilities in Microsoft Exchange Server as part of the mass intrusion campaign publicly known as HAFNIUM, which Microsoft now tracks as Silk Typhoon. The specific victims named in the case include another university in the Southern District of Texas and a law firm with offices worldwide, including in Washington, D.C. Prosecutors say the intruders installed web shells to maintain remote access and searched the law firm's mailboxes using terms including "Chinese sources," "MSS" and "HongKong." The FBI has said the broader HAFNIUM campaign targeted more than 60,000 U.S. entities and successfully victimized more than 12,700 U.S. organizations. Microsoft publicly disclosed the campaign in March 2021, and the United States and partner governments attributed HAFNIUM to China's MSS in July 2021.
The nine-count indictment charges conspiracy to commit wire fraud and two counts of wire fraud; conspiracy to cause damage to and obtain information by unauthorized access to protected computers, and to commit wire fraud and identity theft; two counts of obtaining information by unauthorized access to protected computers; two counts of intentional damage to a protected computer; and aggravated identity theft. According to the Justice Department, the counts carry maximum penalties ranging from two to 20 years in prison. The department notes that an indictment is merely an allegation and that all defendants are presumed innocent until proven guilty beyond a reasonable doubt.
The case then moved to Europe. The indictment was filed under seal in November 2023 and unsealed in July 2025. On July 3, 2025, Xu, then 33, arrived at Milan Malpensa Airport in Italy with his new wife; multiple news outlets reported the couple was traveling on their honeymoon, and Italian police arrested him at the airport at the request of the United States. According to Reuters, Xu's lawyer said at the time that his client was a victim of mistaken identity, and his family said he was an ordinary IT technician.
The extradition fight lasted about nine months. According to Italian media reports, the Milan Court of Appeal ruled the U.S. request admissible on January 27, 2026, Italy's Supreme Court rejected Xu's appeal on April 16, and Italy's Justice Ministry then issued the final authorization. Xu was transferred to U.S. custody on April 25, 2026, and made his initial appearance in federal court in Houston on April 27. He remains in custody, with a detention hearing that had been set for April 30 before U.S. Magistrate Judge Richard W. Bennett. Xu has denied the allegations through an attorney, according to reporting on the extradition.
"The extradition of Xu Zewei demonstrates the FBI's reach extends well beyond U.S. borders," Brett Leatherman, assistant director of the FBI's Cyber Division, said when the extradition was announced. "Xu will now answer for his alleged role in HAFNIUM, a group responsible for a vast intrusion campaign directed by China's Ministry of State Security that compromised more than 12,700 U.S. organizations. He is one of many contractors the Chinese government uses to obscure its hand in cyber operations, and others who do the same face the same risk." Assistant Attorney General for National Security John A. Eisenberg said the United States looks forward "to proving our case in court."
The October 7 reward announcement is the latest step in the case. The RFJ notice says the offer covers information on any person who, acting at the direction or under the control of a foreign government, takes part in malicious cyber activities against U.S. critical infrastructure in violation of the Computer Fraud and Abuse Act, and that it specifically seeks information on Zhang's identification or location, with tips accepted through the program's Tor tip line. The Justice Department has also asked anyone with information about Zhang's whereabouts to contact the FBI at 1-800-CALL-FBI. The case is being investigated by the FBI's Houston Field Office and prosecuted by Assistant U.S. Attorney Mark McIntyre of the Southern District of Texas and Matthew Anzaldi of the National Security Division's National Security Cyber Section.
Since Xu's arrest, his family has kept an account on a Chinese social media platform documenting their wait. According to the family's social media posts, written under the theme "waiting for Bobo's dad to come home," the family has counted the days of his detention — one post marked "day 288 of waiting for Bobo's dad to come home" — and has repeatedly said they believe he is innocent. No trial date for Xu has been publicly announced, and Zhang remains at large.
发布:GSM·美国(发布链接)
图片来源:美国国务院「正义悬赏」计划发布的悬赏海报:最高 1000 万美元征集同案被告 Zhang Yu 的身份或下落线索。图片来源:美国国务院(公共领域)。The U.S. Department of State Rewards for Justice poster offering up to $10 million for information on Zhang Yu. Image: U.S. Department of State (public domain).
GSM Global · 本篇英文版 English edition of this story