司法部在16州协同打击朝鲜远程IT工作者筹资计划、多名中国公民被起诉
2025年6月30日,美国司法部在华盛顿宣布,在全国16个州采取协同执法行动,打击朝鲜政府利用远程IT工作者为其政权筹资的计划。行动包括两份起诉书、一名美国公民被捕、搜查29处已知或涉嫌的“笔记本电脑农场”、查封29个用于清洗非法资金的金融账户和21个欺诈网站,并扣押约200台电脑。
司法部说,这类计划由朝鲜人员使用盗来的和虚假的身份,冒充美国居民获得美国公司的远程IT工作,再把工资收入汇往朝鲜,为其包括武器计划在内的非法项目筹资。协助者分布在美国、中国、阿拉伯联合酋长国和中国台湾地区,受害公司超过100家。一些IT工作者入职后还接触并窃取了雇主的敏感信息,包括受出口管制的美国军事技术和虚拟货币。其中一起计划里,朝鲜IT工作者从佐治亚州亚特兰大一家区块链研发公司窃走了价值逾90万美元的虚拟货币。
在马萨诸塞区的一份五项罪名起诉书中,美国公民 Zhenxing Wang 在新泽西州被捕。起诉书说,他与同伙多年运作的计划为朝鲜IT工作者谋得远程工作、产生逾500万美元收入;同案被起诉的还有中国公民黄靖斌、周宝玉、佟雨泽、徐勇哲、Ziyou Yuan、周震邦,以及台湾居民刘孟婷和 Enchia Liu。另一名美国公民 Kejia Wang 已同意就其角色认罪。起诉书说,2021年至2024年10月间,同伙盗用了80多名美国人的身份,在100多家美国公司获得工作,给受害公司造成至少300万美元的法律费用、网络修复等损失;美国协助者在家中接收和托管公司笔记本电脑、用远程访问设备让境外人员操控,并设立 Hopana Tech LLC 等空壳公司及网站和账户收款,六名已查明的美国协助者共收取至少69.6万美元。一名境外同伙还曾远程侵入加州一家研发超级智能装备技术的国防承包商的电脑,窃取受《国际武器贸易条例》管控的技术数据。行动中,联邦调查局与国防刑事调查局查封了17个域名和29个金融账户。
在佐治亚州北区解封的另一份起诉书中,四名朝鲜公民 Kim Kwang Jin、Kang Tae Bok、Jong Pong Ju 和 Chang Nam Il 被控从两家公司窃取逾90万美元虚拟货币并洗钱。四人曾持朝鲜旅行证件在阿联酋共同作案:其中两人在亚特兰大的区块链公司和一家塞尔维亚虚拟代币公司入职后,分别于2022年2月和3月窃走约17.5万美元和约74万美元虚拟货币,再用混币器 Tornado Cash 清洗赃款。四人目前在逃。
此外,6月10日至17日,联邦调查局在14个州搜查了21处托管笔记本电脑农场的场所,查获约137台笔记本电脑。司法部国家安全司助理部长 John A. Eisenberg 说:“这些计划以美国公司为目标、从美国公司窃取资金,目的是规避制裁、为朝鲜政权的非法项目包括武器计划筹资。”美国国务院已为协助瓦解朝鲜非法金融活动的信息提供最高500万美元奖励。司法部说,这轮行动是其“朝鲜收入生成计划:国内协助者倡议”的一部分。起诉书所载只是指控,所有被告在法庭上被证明有罪之前均推定无罪。
(来源:美国司法部)
DOJ Announces Coordinated Actions in 16 States Against North Korean Remote IT Worker Revenue Schemes
On June 30, 2025, the Justice Department in Washington announced coordinated actions across 16 states against the North Korean government’s schemes to fund its regime through remote information technology work for U.S. companies. The actions include two indictments, an arrest, searches of 29 known or suspected “laptop farms,” and the seizure of 29 financial accounts used to launder illicit funds, 21 fraudulent websites, and approximately 200 computers.
According to the Department, North Korean individuals used stolen and fake identities to pose as U.S. residents and obtain remote IT jobs at more than 100 U.S. companies, assisted by individuals in the United States, China, the United Arab Emirates, and Taiwan. Once employed, the workers received regular salary payments that were funneled to the North Korean regime, and in some cases they stole sensitive employer information, including export-controlled U.S. military technology and virtual currency. In one scheme, North Korean IT workers stole virtual currency worth more than $900,000 from an Atlanta, Georgia-based blockchain research and development company.
In a five-count indictment in the District of Massachusetts, U.S. national Zhenxing “Danny” Wang of New Jersey was arrested. The indictment describes a multiyear scheme that generated more than $5 million in revenue. Also charged are Chinese nationals Jing Bin Huang, Baoyu Zhou, Tong Yuze, Yongzhe Xu, Ziyou Yuan, and Zhenbang Zhou, and Taiwanese nationals Mengting Liu and Enchia Liu. A second U.S. national, Kejia “Tony” Wang, agreed to plead guilty. From about 2021 to October 2024, the conspirators allegedly compromised the identities of more than 80 U.S. persons to obtain jobs at more than 100 companies, causing at least $3 million in legal, remediation, and other losses. U.S. facilitators hosted company laptops at their homes, enabled remote access through keyboard-video-mouse switches, and created shell companies such as Hopana Tech LLC, receiving at least $696,000 in total. An overseas co-conspirator also accessed a California defense contractor’s files and stole technical data controlled under the International Traffic in Arms Regulations. The FBI and the Defense Criminal Investigative Service seized 17 web domains and 29 financial accounts.
In a second indictment unsealed in the Northern District of Georgia, four North Korean nationals, Kim Kwang Jin, Kang Tae Bok, Jong Pong Ju, and Chang Nam Il, were charged with stealing virtual currency valued at more than $900,000 from two companies and laundering the proceeds. Working as a co-located team in the United Arab Emirates, two of them were hired by the Atlanta blockchain company and a Serbian virtual token company and, in February and March 2022, stole about $175,000 and about $740,000 in virtual currency, laundering the funds through the mixer Tornado Cash. The four remain at large.
Between June 10 and 17, 2025, the FBI also searched 21 premises across 14 states hosting laptop farms, seizing approximately 137 laptops. “These schemes target and steal from U.S. companies and are designed to evade sanctions and fund the North Korean regime’s illicit programs, including its weapons programs,” said Assistant Attorney General John A. Eisenberg of the National Security Division. The State Department has offered rewards of up to $5 million for information helping disrupt North Korea’s illicit financial activities. The Department said the actions are part of its DPRK RevGen: Domestic Enabler Initiative. The charges are merely allegations, and all defendants are presumed innocent until proven guilty beyond a reasonable doubt in a court of law.
(Source: U.S. Department of Justice)
来源:美国司法部
发布:GSM·美国(发布链接)
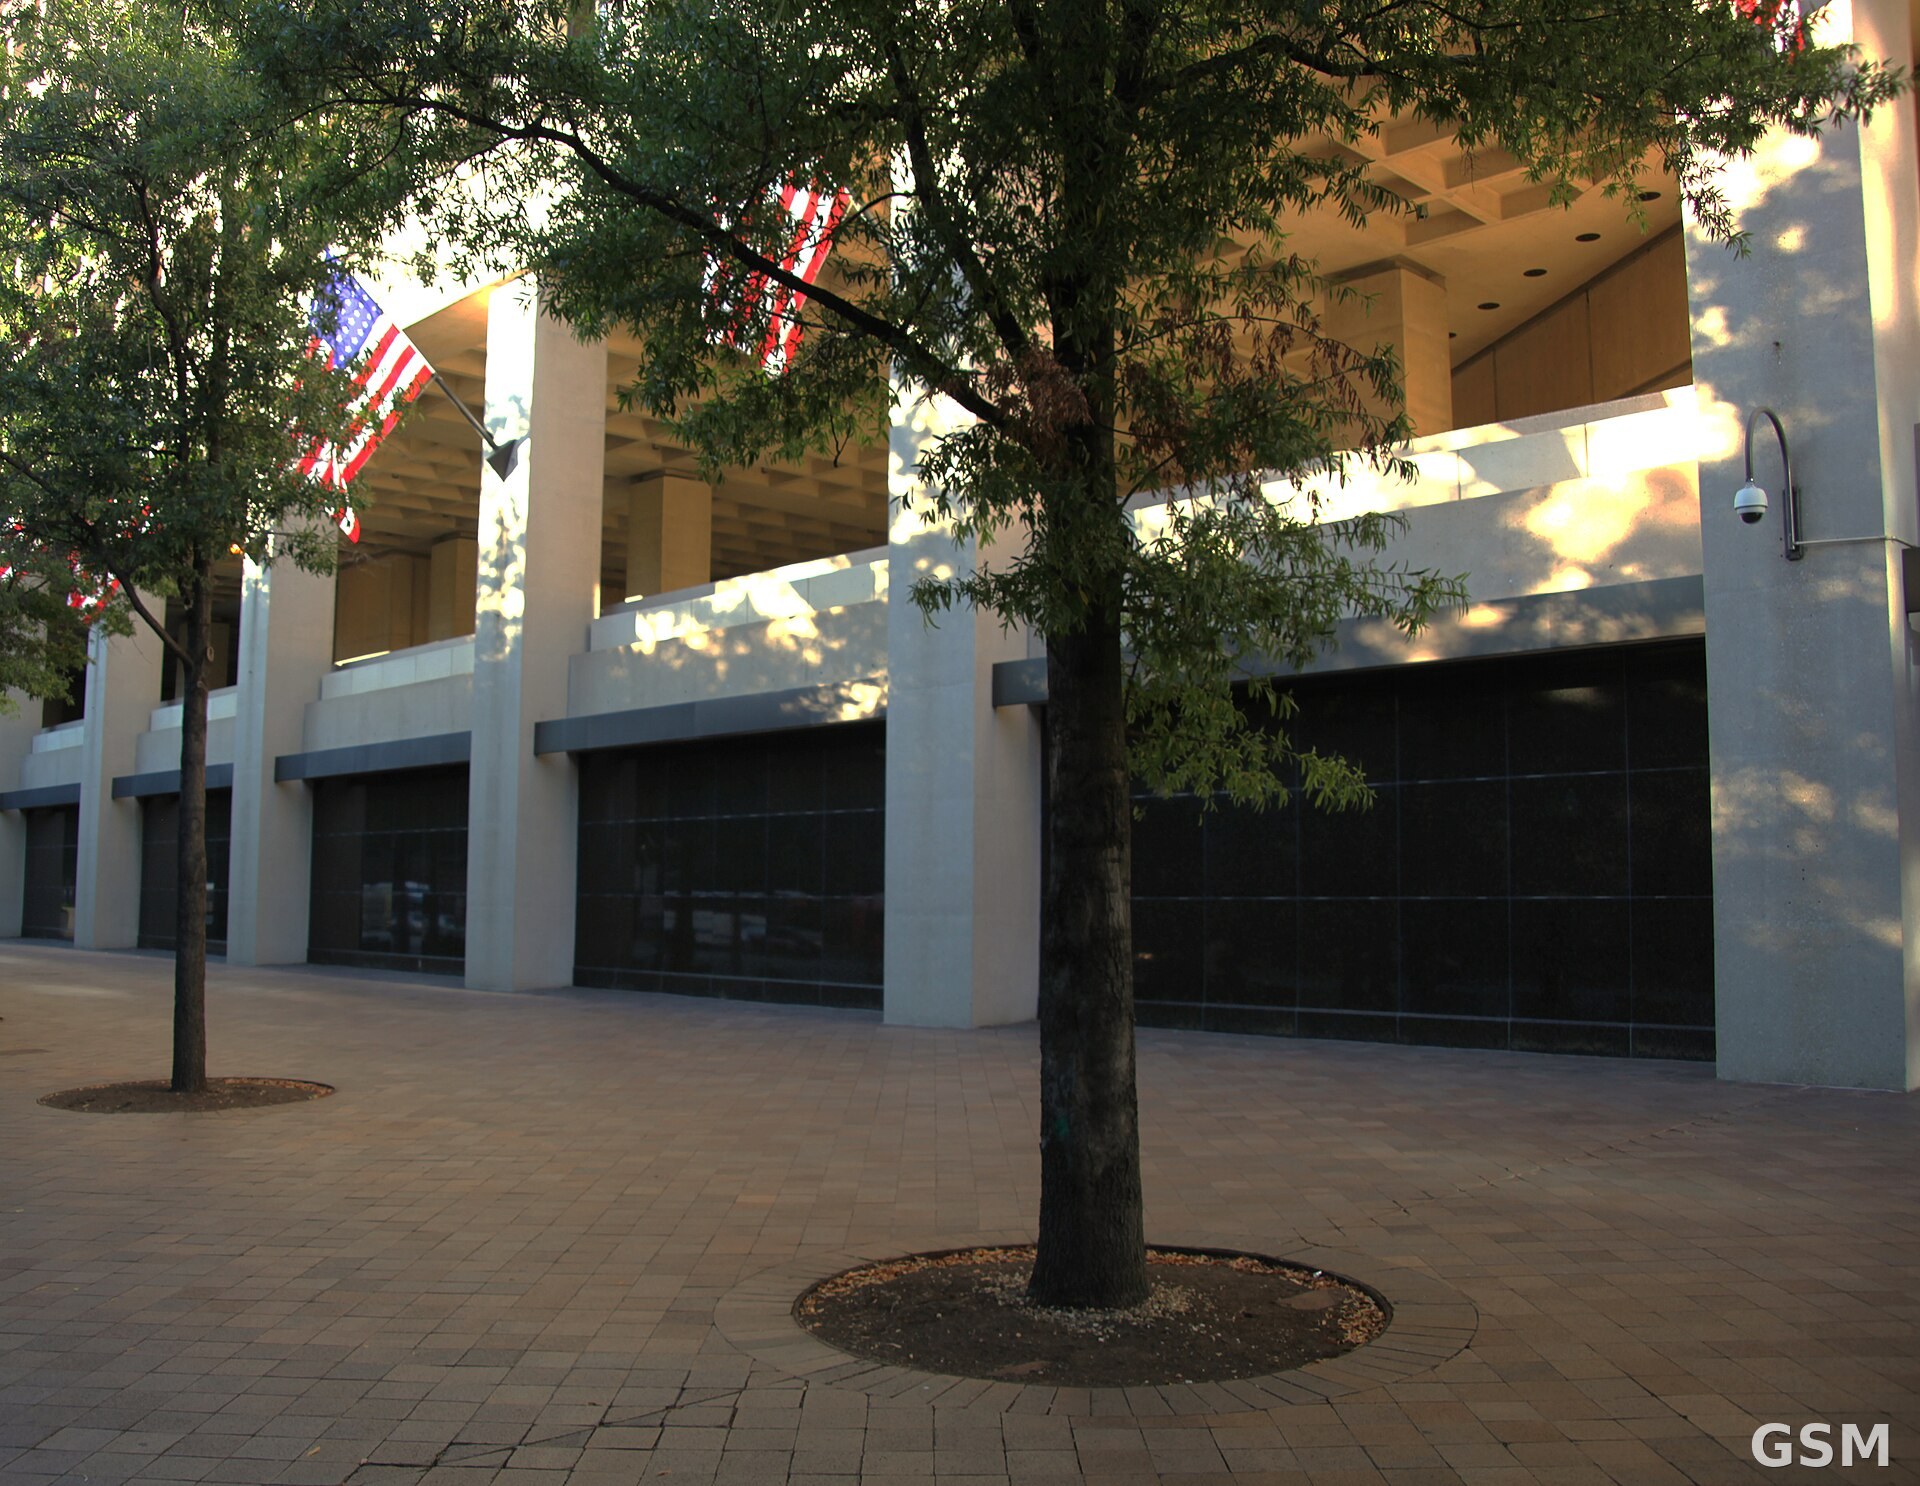
图片来源:图:位于华盛顿的联邦调查局总部 J. Edgar Hoover Building 南侧外景,联邦调查局是本轮全国协同行动的主要执行机构之一。Tim Evanson 摄,CC BY-SA 2.0,经 Wikimedia Commons。 / Photo: The south side of the J. Edgar Hoover Building in Washington, headquarters of the FBI, one of the lead agencies in the nationwide actions. Photo by Tim Evanson, CC BY-SA 2.0, via Wikimedia Commons.
GSM Global · 本篇英文版 English edition of this story