司法部打击朝鲜加密货币盗窃:查封 FaceStealer 基础设施,获准扣押币安被盗资产逾12亿美元
美国司法部11月12日宣布多项协调行动,打击朝鲜政府靠大规模盗窃加密货币为其政权筹资的做法。行动包括查封「FaceStealer」社交工程骗局所用的云端基础设施,该骗局已盗走价值逾4亿美元的加密货币;司法部同时获得法院授权,可扣押或限制近期从加密货币交易所币安(Binance)被盗的逾12亿美元加密货币。
国家安全事务首席副助理司法部长 M. Scott Proctor 说,朝鲜政府靠加密货币盗窃为其非法政权与非法武器计划筹资,今天的公告显示美国将反击该政权靠网络犯罪牟利的做法,国家安全司将动用一切工具扣押并返还朝鲜的不义之财。刑事司助理司法部长 A. Tysen Duva 说,刑事司的计算机犯罪与知识产权科与执法伙伴在第一时间冻结了数十亿美元被盗的币安数字资产。
在加州中区公布的 FaceStealer 一腿中,朝鲜黑客以 Sapphire Sleet、APT38、BlueNoroff、Stardust Chollima 等公开代号活动,用从先前受害者处盗来的账号发出视频会议邀请,暗中录下参会者的网络摄像头画面,再播放先前受害者的录像或用超级智能(SI)制作的深伪视频,冒充受害者信任的人取信对方,随后以「修复技术故障」为名诱使对方安装恶意软件,进而盗窃加密货币或侵入其设备。过去18个月,该骗局盗走逾4亿美元,受害者多在加密货币与 Web3 行业,近期还越来越多地盯上开源软件开发者,图谋供应链攻击。联邦调查局(FBI)凭联邦搜查令查获了900多段 FaceStealer 受害者的网络摄像头录像,并发布了防范报告与专题网站。
币安一腿中,FBI 称为「TraderTraitor」的朝鲜军方成员于10月29日前后从币安盗走价值逾60亿美元的虚拟资产。此后美国政府与私营部门合作已冻结逾27亿美元,司法部已获法院授权扣押或限制其中逾12亿美元。追踪、冻结与没收工作仍在进行,朝鲜方面仍在通过跨链桥、混币器与交易所清洗这批资产。
Justice Department Disrupts North Korea Crypto Theft: FaceStealer Infrastructure Seized, Over $1.2 Billion in Stolen Binance Assets Cleared for Seizure
The U.S. Department of Justice announced coordinated actions on November 12 against the North Korean government's schemes to fund its regime through the massive theft of cryptocurrency. The actions include the seizure of cloud-based infrastructure used in the FaceStealer social engineering scheme, which has resulted in the theft of more than $400 million worth of cryptocurrency, and court-authorized seizure and restraint of more than $1.2 billion worth of cryptocurrency recently stolen from Binance, a virtual currency exchange.
Principal Deputy Assistant Attorney General for National Security M. Scott Proctor said North Korea's government bankrolls its rogue regime and illicit weapons program through cryptocurrency theft, and that the National Security Division will use every tool at its disposal to seize and return North Korea's ill-gotten gains. Assistant Attorney General A. Tysen Duva of the Criminal Division said the division's Computer Crime and Intellectual Property Section and law enforcement partners immediately froze billions of dollars' worth of stolen Binance digital assets.
In the FaceStealer action announced in the Central District of California, North Korean hackers known publicly as Sapphire Sleet, APT38, BlueNoroff and Stardust Chollima, among other names, lured targets with video meeting invitations sent from accounts stolen from prior victims, secretly recorded targets' webcam video, and played prerecorded or super intelligence (SI) deepfake videos to impersonate trusted contacts. They then introduced a fake technical error and induced targets to install malware, stealing cryptocurrency or compromising devices. The scheme has stolen more than $400 million in the last 18 months, targeting people in the cryptocurrency and Web3 industries and, increasingly, open-source software developers in an apparent bid to enable supply-chain attacks. Pursuant to a federal warrant, the FBI seized over 900 webcam videos of FaceStealer victims and published a report and resource site on the scheme.
Separately, members of the North Korean military referred to by the FBI as TraderTraitor stole more than $6 billion worth of virtual assets from Binance on or about October 29. Collective U.S. government and private-sector efforts have since frozen more than $2.7 billion, with court authorization already obtained to seize or restrain more than $1.2 billion of that amount. Efforts to trace, freeze, seize and forfeit the stolen assets are ongoing as the actors continue laundering them through bridges, mixers and exchanges.
来源:美国司法部
发布:GSM·美国(发布链接)
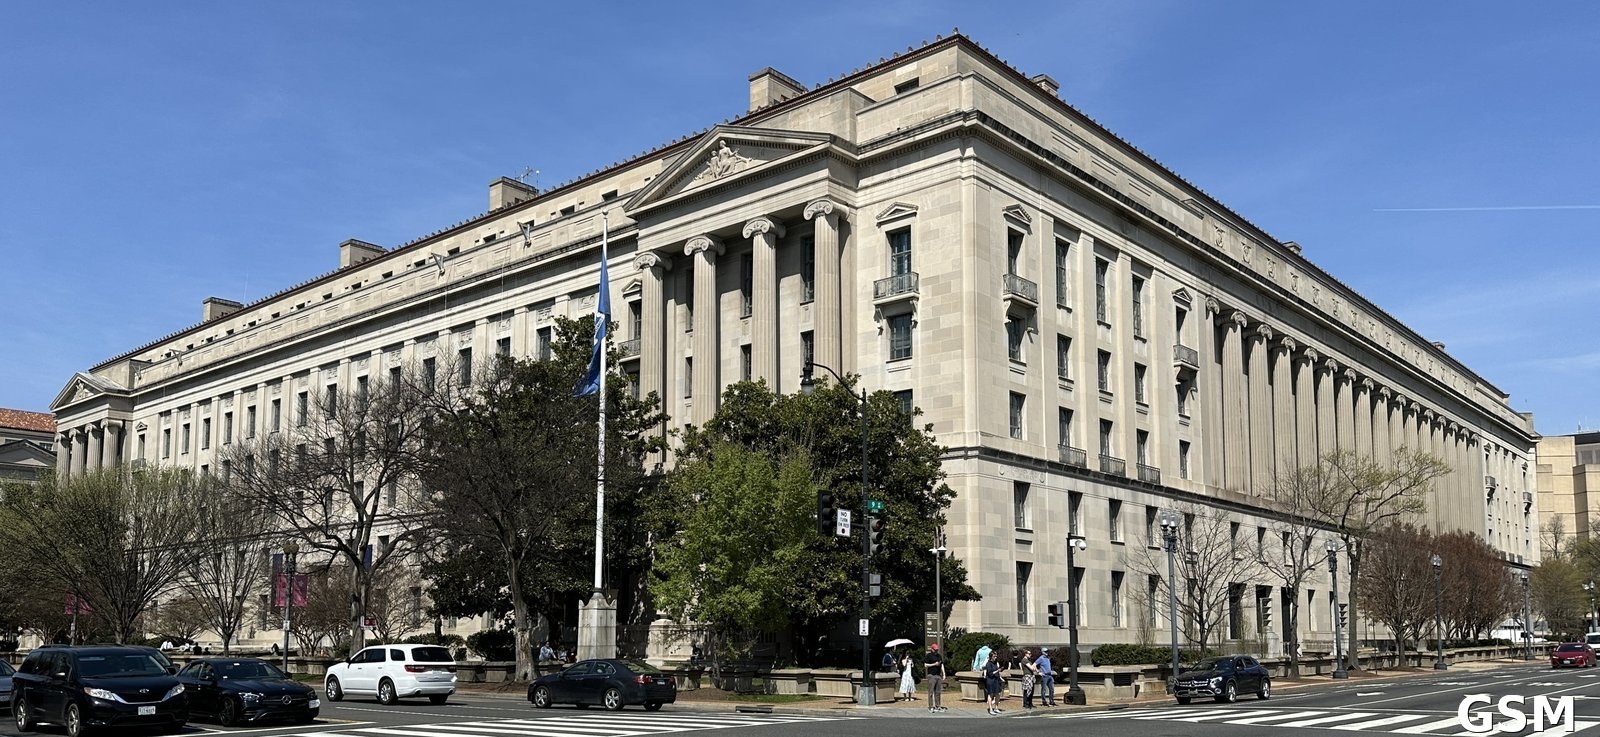
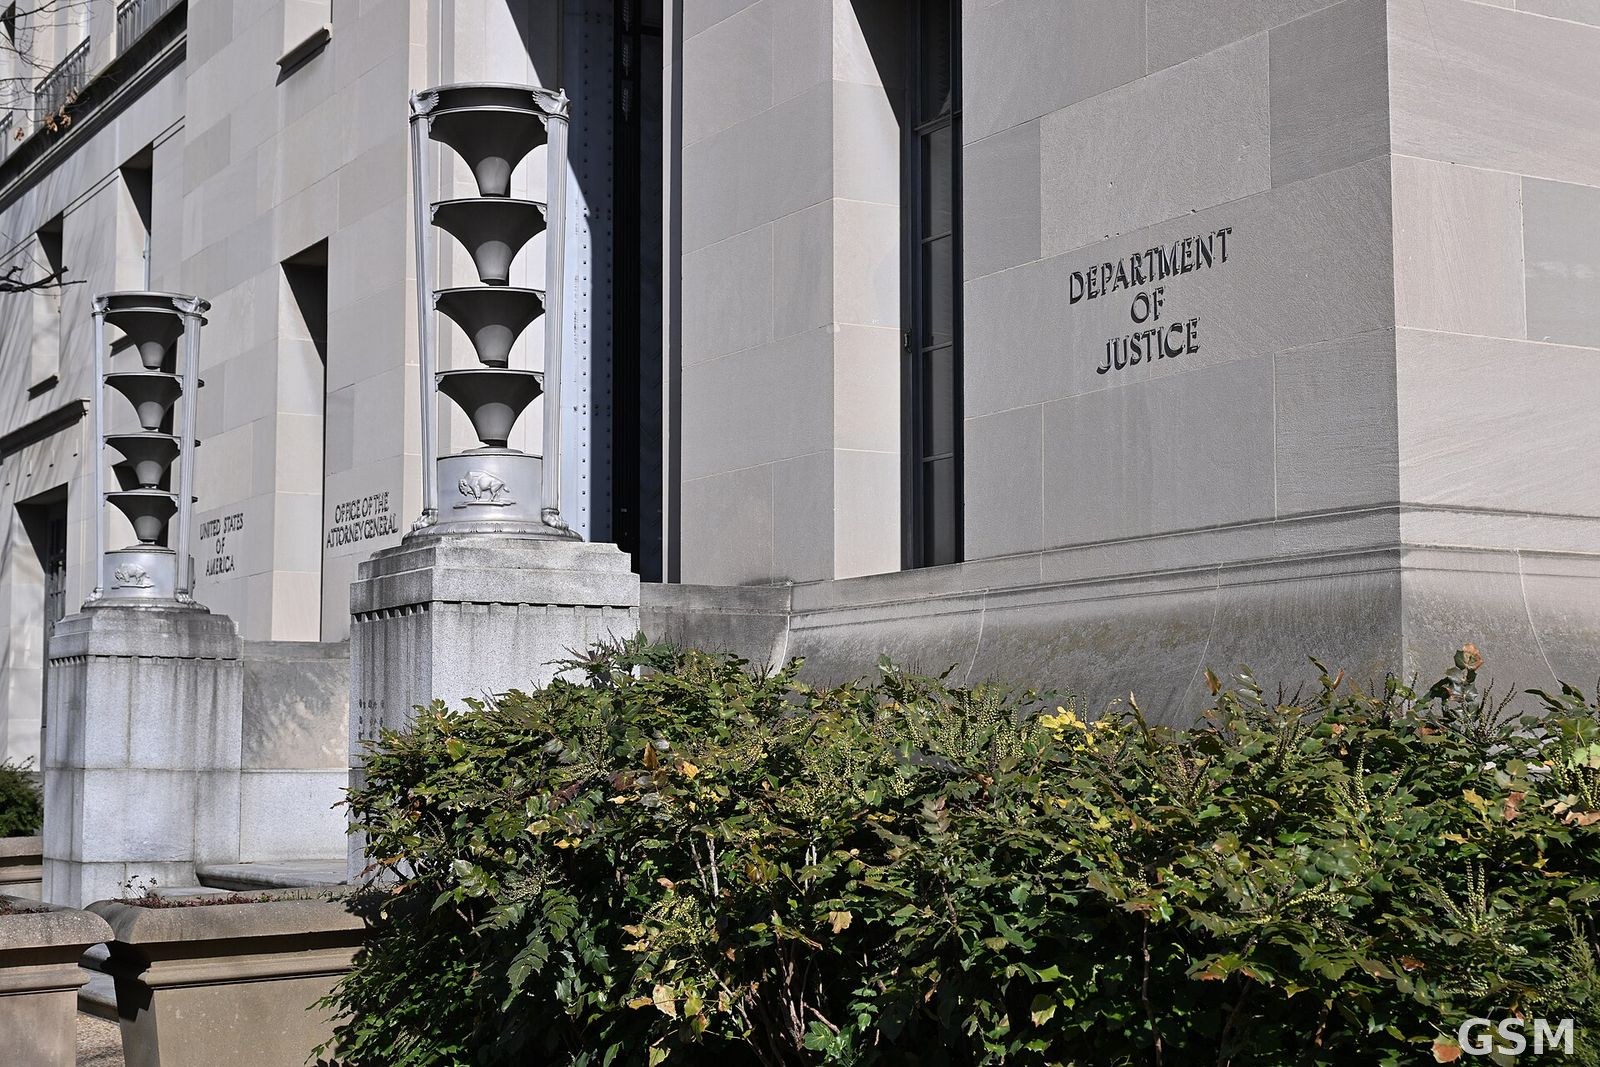
图片来源:图:美国司法部总部大楼。固定图库联邦核心包,公共领域。 / Photo: U.S. Department of Justice headquarters. Federal core asset pack, public domain.
GSM Global · 本篇英文版 English edition of this story