谷歌云推出 Agent Compute Engine:每个智能体独享硬件隔离微型虚拟机,Agent Substrate 1.0 同步在 GKE 正式商用
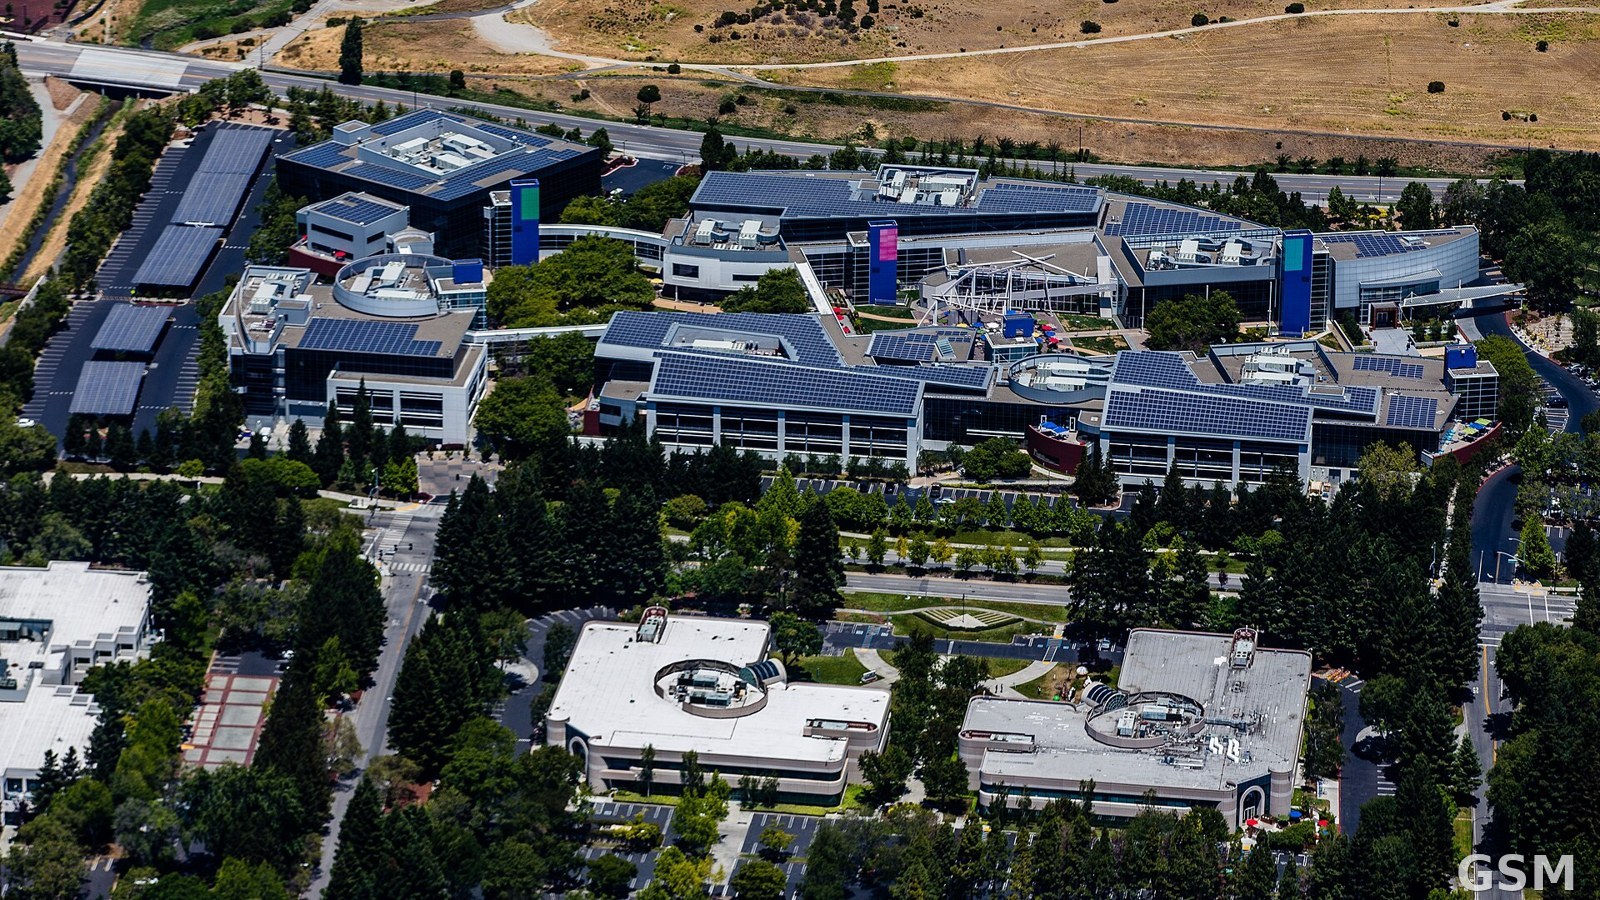
谷歌云在 AGNTCon + MCPCon 大会期间宣布推出 Agent Compute Engine,这是一项专为智能体打造的计算服务,目前已在支撑 Gemini 作为工作任务智能体的运行。谷歌称,该服务将在未来数月内以预览形式向客户开放,提供硬件隔离的运行时沙箱安全。谷歌云总部位于加利福尼亚州圣克拉拉县山景城。
按谷歌的说明,Agent Compute Engine 源于谷歌自身大规模智能体负载的需求:这类负载要写代码并执行、调用工具、驱动浏览器、编排企业工作流,并以很高的频次快速迭代。服务为每个智能体分配一台高性能、安全的专属「计算机」:微型虚拟机快速启动,借助写时复制(copy-on-write)的内存共享让多个智能体共用同一操作系统模板,空闲的微型虚拟机则通过快速检查点与恢复机制暂停。安全方面,该服务与谷歌的 Titanium 卸载基础设施配合,通过硬件隔离的 Cloud Hypervisor 边界提供纵深防御,每个微型虚拟机有自己的来宾内核与根权限;每个微型虚拟机运行智能体自身的身份、使用短期凭据,并拥有经密码学验证的独立 ID,服务凭据在微型虚拟机之外的出口处注入,凭据不进入沙箱本身。每个微型虚拟机还配有自己的 Hyperdisk,以持久保存执行工作区与智能体上下文。
同期宣布的还有开源运行时 Agent Substrate:谷歌称 Agent Substrate、gVisor 与 OpenRL 已被云原生计算基金会(CNCF)接纳进入 Sandbox 阶段,Agent Substrate 已达到 1.0 版本并在 Google Kubernetes Engine(GKE)上正式商用。按谷歌的说明,Agent Substrate 把有状态的智能体与计算分离,空闲智能体可快照存入存储、并在 500 毫秒以内恢复,容器密度最高可达原来的 10 倍。谷歌同时扩大了智能体治理工具的覆盖范围,使其涵盖运行在谷歌云各服务及其他环境中的智能体。Gemini 副总裁兼 Google Fellow Gautham Thambidorai 在公告中表示,Agent Compute Engine 的微型虚拟机为谷歌提供了把交互式智能体沙箱交付全球用户所需的响应速度、硬件隔离与负载密度。谷歌未在公告中公布 Agent Compute Engine 的定价。
Google Cloud Launches Agent Compute Engine: A Hardware-Isolated MicroVM for Every Agent, With Agent Substrate 1.0 Generally Available on GKE
Google Cloud used the AGNTCon + MCPCon event to launch Agent Compute Engine, a purpose-built compute service that already powers Gemini as an agent for work tasks. Google said the service will be available in preview in the coming months, providing hardware-isolated runtime sandbox security. Google Cloud is headquartered in Mountain View, Santa Clara County, California.
Google said Agent Compute Engine arose from the need to handle its own massive agentic workloads, which write and execute code, run tools, drive browsers, orchestrate enterprise workflows and iterate rapidly and at scale. The service gives every agent its own high-performance, secure computer: microVMs boot rapidly, copy-on-write memory sharing lets multiple agents run on a single operating system template, and idle microVMs are paused via fast checkpoint and restore. On security, the service runs with Titanium, Google's offload infrastructure processing unit, delivering silicon-rooted defense-in-depth for untrusted AI agents through a hardware-isolated Cloud Hypervisor boundary with its own guest kernel and root access. Each microVM runs its agent's own identity using short-lived credentials, carries its own cryptographically verified ID, and has service credentials injected in egress outside the microVM, so credentials stay outside the sandbox. Each microVM also gets its own Hyperdisk, enabling persistence of execution workspaces and agent context.
Alongside the managed service, Google announced that Agent Substrate, gVisor and OpenRL have been accepted into the CNCF Sandbox, and that Agent Substrate has reached 1.0 and is generally available on Google Kubernetes Engine (GKE). Google said Agent Substrate separates stateful agents from compute by snapshotting idle agents to storage and restoring them in under 500 milliseconds, achieving up to 10 times container density. Google also expanded its agent governance tools to cover agents across its own services and other environments. Gautham Thambidorai, vice president and Google Fellow for Gemini, said Agent Compute Engine microVMs give Google the responsiveness, hardware isolation and workload density needed to deliver interactive agent sandboxes to users around the world. Google listed no pricing for Agent Compute Engine in the announcement.
来源:谷歌云
发布:GSM·美国(发布链接)
图片来源:图:谷歌山景城园区。Austin McKinley 摄,CC BY 3.0,经 Wikimedia Commons。 / Photo: The Google campus in Mountain View, California. Photo by Austin McKinley, CC BY 3.0, via Wikimedia Commons.
GSM Global · 本篇英文版 English edition of this story