卫生与公众服务部与宾州Lehigh Valley医疗网络达成80万美元和解:勒索软件事件外泄248,359人健康信息
美国卫生与公众服务部(Department of Health and Human Services,HHS)民权办公室(Office for Civil Rights,OCR)10月29日在华盛顿宣布,已与宾夕法尼亚州医疗系统 Lehigh Valley Health Network(LVHN)及其关联受保实体达成和解,解决该机构涉嫌违反《健康保险流通与责任法案》(HIPAA)隐私、安全与泄露通知规则的调查。LVHN 同意支付 80 万美元,并执行一项为期三年的纠正行动计划,由 OCR 监督。
这是 OCR 第 22 起勒索软件执法行动。据 HHS 公布,LVHN 于 2023 年 5 月 15 日提交泄露报告,称该机构在 2023 年 2 月 4 日发现其信息系统出现可疑活动,后确认系勒索软件攻击。攻击中,受保护健康信息(PHI)被窃取并发布到暗网上,受影响人数达 248,359 人。
外泄信息包括正在接受放射肿瘤治疗的癌症患者的敏感照片,以及受影响个人的姓名、地址、出生日期、社会安全号码、驾驶执照号码、财务信息、诊断与病情、实验室结果、用药与治疗信息。
OCR 在调查中认定,LVHN 涉嫌存在多项违规:未对其全部电子受保护健康信息的保密性、完整性与可用性所面临的风险与漏洞进行准确、全面的风险分析;未建立定期审查信息系统活动记录(如审计日志、访问报告与安全事件跟踪报告)的程序;不当披露了 248,359 人的受保护健康信息;未及时通知受影响个人;也未及时通知 HHS 部长。
根据纠正行动计划,LVHN 承诺采取以下措施:开展准确、全面的风险分析,确定其电子受保护健康信息面临的潜在风险与漏洞;制定并实施风险管理计划,处理和缓解风险分析中发现的安全风险与漏洞;审查并在必要时修订现行隐私、安全与泄露通知规则方面的政策与程序;审查并按需要制定或修订面向全体员工的 HIPAA 规则培训材料。
OCR 主任 Paula M. Stannard 说:「未能进行准确、全面的风险分析、未能定期审查信息系统活动,会使受监管实体成为网络攻击的诱人目标。抵御网络攻击的最佳防线,是全面落实 HIPAA 安全规则。」
HHS 同时向医疗机构、健康计划、医疗信息交换中心及其业务伙伴提出防范建议,包括摸清电子受保护健康信息在本机构的位置与流转路径、定期开展并更新风险分析、落实审计控制、定期审查信息系统活动、对用户身份进行认证、对传输中与静态的电子受保护健康信息加密、把事件教训纳入机构整体安全管理流程,并为员工提供与其岗位相符的定期 HIPAA 培训。
HHS Settles Ransomware Investigation of Lehigh Valley Health Network for $800,000 After Breach Affecting 248,359 People
The Office for Civil Rights (OCR) of the U.S. Department of Health and Human Services (HHS) announced in Washington on October 29 that it has reached a settlement with Lehigh Valley Health Network (LVHN), a health system in Pennsylvania, and its affiliated covered entities, resolving an investigation into potential violations of the HIPAA Privacy, Security, and Breach Notification Rules. LVHN agreed to pay $800,000 and to implement a corrective action plan that OCR will monitor for three years.
The settlement marks OCR's 22nd ransomware enforcement action. According to HHS, LVHN filed a breach report on May 15, 2023, stating that on February 4, 2023, it discovered suspicious activity in its IT system that was later determined to be ransomware. Protected health information (PHI) was exfiltrated and posted on the dark web, affecting 248,359 individuals.
The information involved included sensitive photographs of cancer patients receiving radiation oncology treatment, as well as names, addresses, dates of birth, Social Security numbers, driver's license numbers, financial information, diagnoses and conditions, lab results, medications, and treatment information.
OCR found that LVHN had potentially violated the rules by failing to conduct an accurate and thorough risk analysis of the risks and vulnerabilities to all of its electronic PHI; failing to implement procedures to regularly review records of information system activity such as audit logs, access reports, and security incident tracking reports; impermissibly disclosing the PHI of 248,359 individuals; failing to timely notify affected individuals; and failing to timely notify the Secretary of HHS.
Under the corrective action plan, LVHN committed to conduct an accurate and thorough risk analysis, develop and implement a risk management plan, review and revise its Privacy, Security, and Breach Notification Rule policies and procedures as needed, and review and revise its HIPAA training materials for workforce members.
"Failure to conduct an accurate and thorough risk analysis and to undertake regular review of information system activity makes regulated entities attractive targets for cyberattacks," said OCR Director Paula M. Stannard. "The best defense against cyberattacks is full implementation of the HIPAA Security Rule."
HHS also recommended that regulated entities identify where electronic PHI is located and how it flows through their systems, periodically conduct and update risk analyses, ensure audit controls are in place, regularly review information system activity, authenticate users, encrypt electronic PHI in transit and at rest, incorporate lessons learned from incidents into their security management processes, and provide workforce members with regular HIPAA training specific to their job duties.
来源:GSM·美国(原文链接)
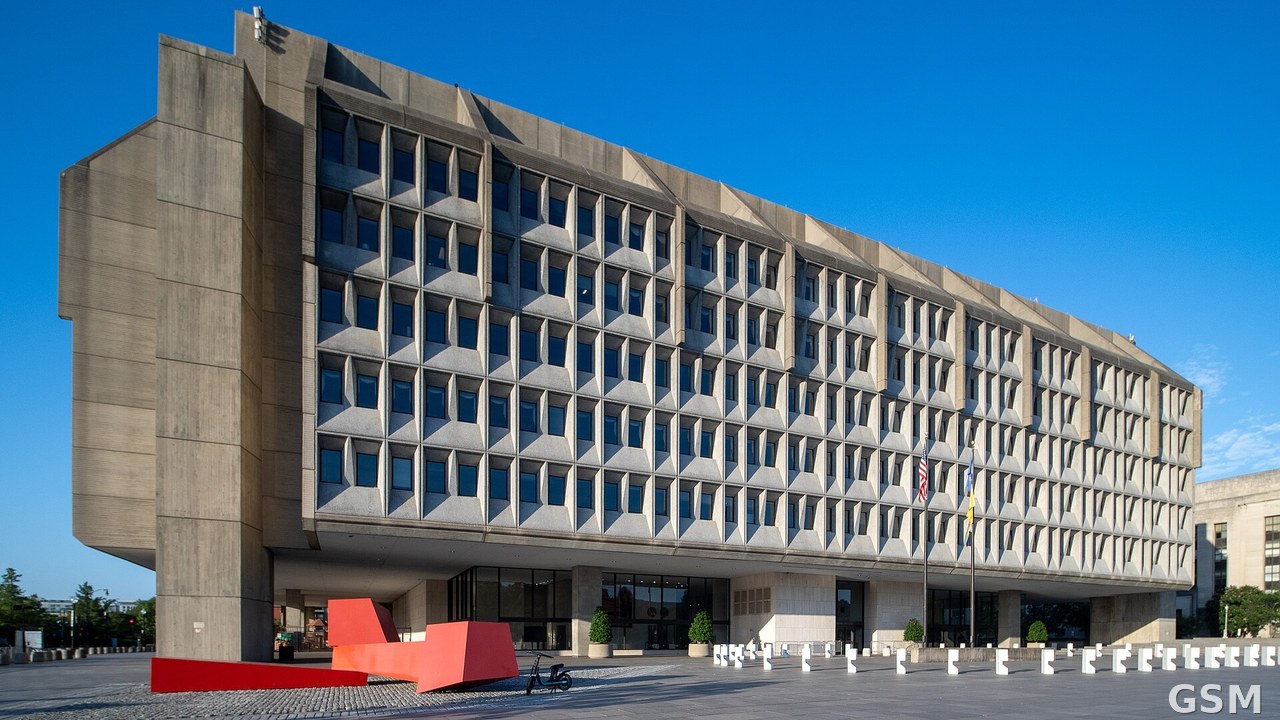
图片来源:图:位于华盛顿的美国卫生与公众服务部总部 Hubert H. Humphrey 大楼外景。ajay_suresh 摄,经 Wikimedia Commons,授权 CC BY 2.0。 / Photo: The Hubert H. Humphrey Building, headquarters of the U.S. Department of Health and Human Services in Washington. Photo by ajay_suresh, via Wikimedia Commons, CC BY 2.0.