司法部查封 LummaC2 窃密恶意软件的五个域名:联邦调查局已查明至少170万次窃取信息行为
美国司法部2025年5月21日宣布,两份授权查封五个互联网域名的令状已经解封;这些域名被恶意网络行为者用来运营窃密恶意软件服务 LummaC2,本案调查由位于德克萨斯州达拉斯县的联邦调查局 Dallas 外勤办公室负责。
司法部国家安全司司长 Sue J. Bai 说,司法部将继续动用其独有工具、权限与伙伴关系打击恶意网络行动与犯罪网络,这次打击是检方、探员与私营部门伙伴合力保护美国免受持续网络安全威胁的又一实例。司法部刑事司司长 Matthew R. Galeotti 说,LummaC2 这类恶意软件被用来从数以百万计的受害者处窃取登录凭据等敏感信息,以助长欺诈性银行转账与加密货币盗窃等一系列犯罪,司法部决心以法院命令的打击行动保护公众的个人信息与资产。联邦调查局网络司助理局长 Bryan Vorndran 说,LummaC2 是网络犯罪市场上最受欢迎的窃密服务、对受害者发动了数以百万计的攻击,联邦调查局与伙伴一道打击了其基础设施并查封了用户面板。
司法部称,支持查封令状的宣誓书指,LummaC2 的管理员利用被查封的网站向其下线与其他网络犯罪分子分发这款窃密软件。法院文件称,使用这类恶意软件的犯罪分子常盯上的目标包括浏览器数据、自动填充信息、登录邮箱与银行服务的凭据,以及可打开加密货币钱包的加密货币助记词。宣誓书指,联邦调查局已查明至少170万次有人使用 LummaC2 窃取这类信息的实例。
被查封的域名也称用户面板,是 LummaC2 恶意软件的登录页面,供有凭据的用户与管理员访问和部署该软件。2025年5月19日,美国政府查封了其中两个域名;5月20日,LummaC2 管理员告知用户其已设立三个新域名托管用户面板;次日,美国政府又查封了这三个新域名。司法部称,查封将阻止域名所有者与网络犯罪分子利用这些网站访问 LummaC2、入侵电脑并窃取受害者信息;现在访问这些网站的人会看到司法部(包括联邦调查局)已查封该站的提示。
与司法部当天的行动同步,微软宣布了一项独立民事行动,要关停另有2,300个据称被 LummaC2 行为者或其代理人使用的互联网域名。本案由德克萨斯州北区联邦检察官办公室、司法部国家安全司国家安全网络科与刑事司计算机犯罪与知识产权科承办。司法部并提醒,国务院「正义奖励」计划对提供与外国政府有关联、针对美国关键基础设施实施特定恶意网络活动者信息的人,最高可奖励1,000万美元;认为自己电脑或设备已遭入侵的人可向联邦调查局互联网犯罪投诉中心报告。(来源:美国司法部)
Justice Department Seizes Five Domains Behind the LummaC2 Information-Stealing Malware Service: FBI Has Identified at Least 1.7 Million Thefts
The Justice Department announced on May 21, 2025, the unsealing of two warrants authorizing the seizure of five internet domains used by malicious cyber actors to operate the LummaC2 information-stealing malware service; the investigation is led by the FBI's Dallas Field Office in Dallas County, Texas.
"The Department will continue to use its unique tools, authorities, and partnerships to disrupt malicious cyber operations and criminal networks," said Sue J. Bai, head of the Justice Department's National Security Division, calling the disruption another instance of prosecutors, agents and private-sector partners coming together against persistent cybersecurity threats. Matthew R. Galeotti, head of the Criminal Division, said malware like LummaC2 is deployed to steal sensitive information such as user login credentials from millions of victims to facilitate crimes including fraudulent bank transfers and cryptocurrency theft, and that the Department is resolved to use court-ordered disruptions to protect the public's personal information and assets. Assistant Director Bryan Vorndran of the FBI's Cyber Division said LummaC2 was the most popular infostealer service available in online criminal markets, responsible for millions of attacks, and that the FBI and its partners disrupted its infrastructure and seized its user panels.
As alleged in the affidavits filed in support of the seizure warrants, the administrators of LummaC2 used the seized websites to distribute the malware to their affiliates and other cyber criminals. According to court documents, common targets include browser data, autofill information, login credentials for email and banking services, and cryptocurrency seed phrases, which permit access to virtual currency wallets. The FBI has identified at least 1.7 million instances where LummaC2 was used to steal this type of information, the affidavits allege.
The seized domains, also referred to as user panels, served as login pages for LummaC2, allowing credentialed users and administrators to access and deploy it. On May 19, 2025, the government seized two domains. On May 20, as detailed in court documents, the LummaC2 administrators told their users of three new domains they had set up to host the user panel; the next day, the government seized those three domains as well. The seizure will prevent the owners and cyber criminals from using the websites to access LummaC2 to compromise computers and steal victim information, the Department said; visitors to the sites will now see a message that the site has been seized by the Justice Department, including the FBI.
Concurrent with the Department's actions, Microsoft announced an independent civil action to take down 2,300 internet domains also claimed to be used by the LummaC2 actors or their proxies. The U.S. Attorney's Office for the Northern District of Texas, the National Security Division's National Security Cyber Section, and the Criminal Division's Computer Crime and Intellectual Property Section are handling the case. The Department also noted that the State Department's Rewards for Justice program offers up to $10 million for information on foreign government-linked individuals engaged in certain malicious cyber activities against U.S. critical infrastructure, and that anyone who believes a computer or device has been compromised can report it to the FBI's Internet Crime Complaint Center. (Source: U.S. Department of Justice)
来源:美国司法部
发布:GSM·美国(发布链接)
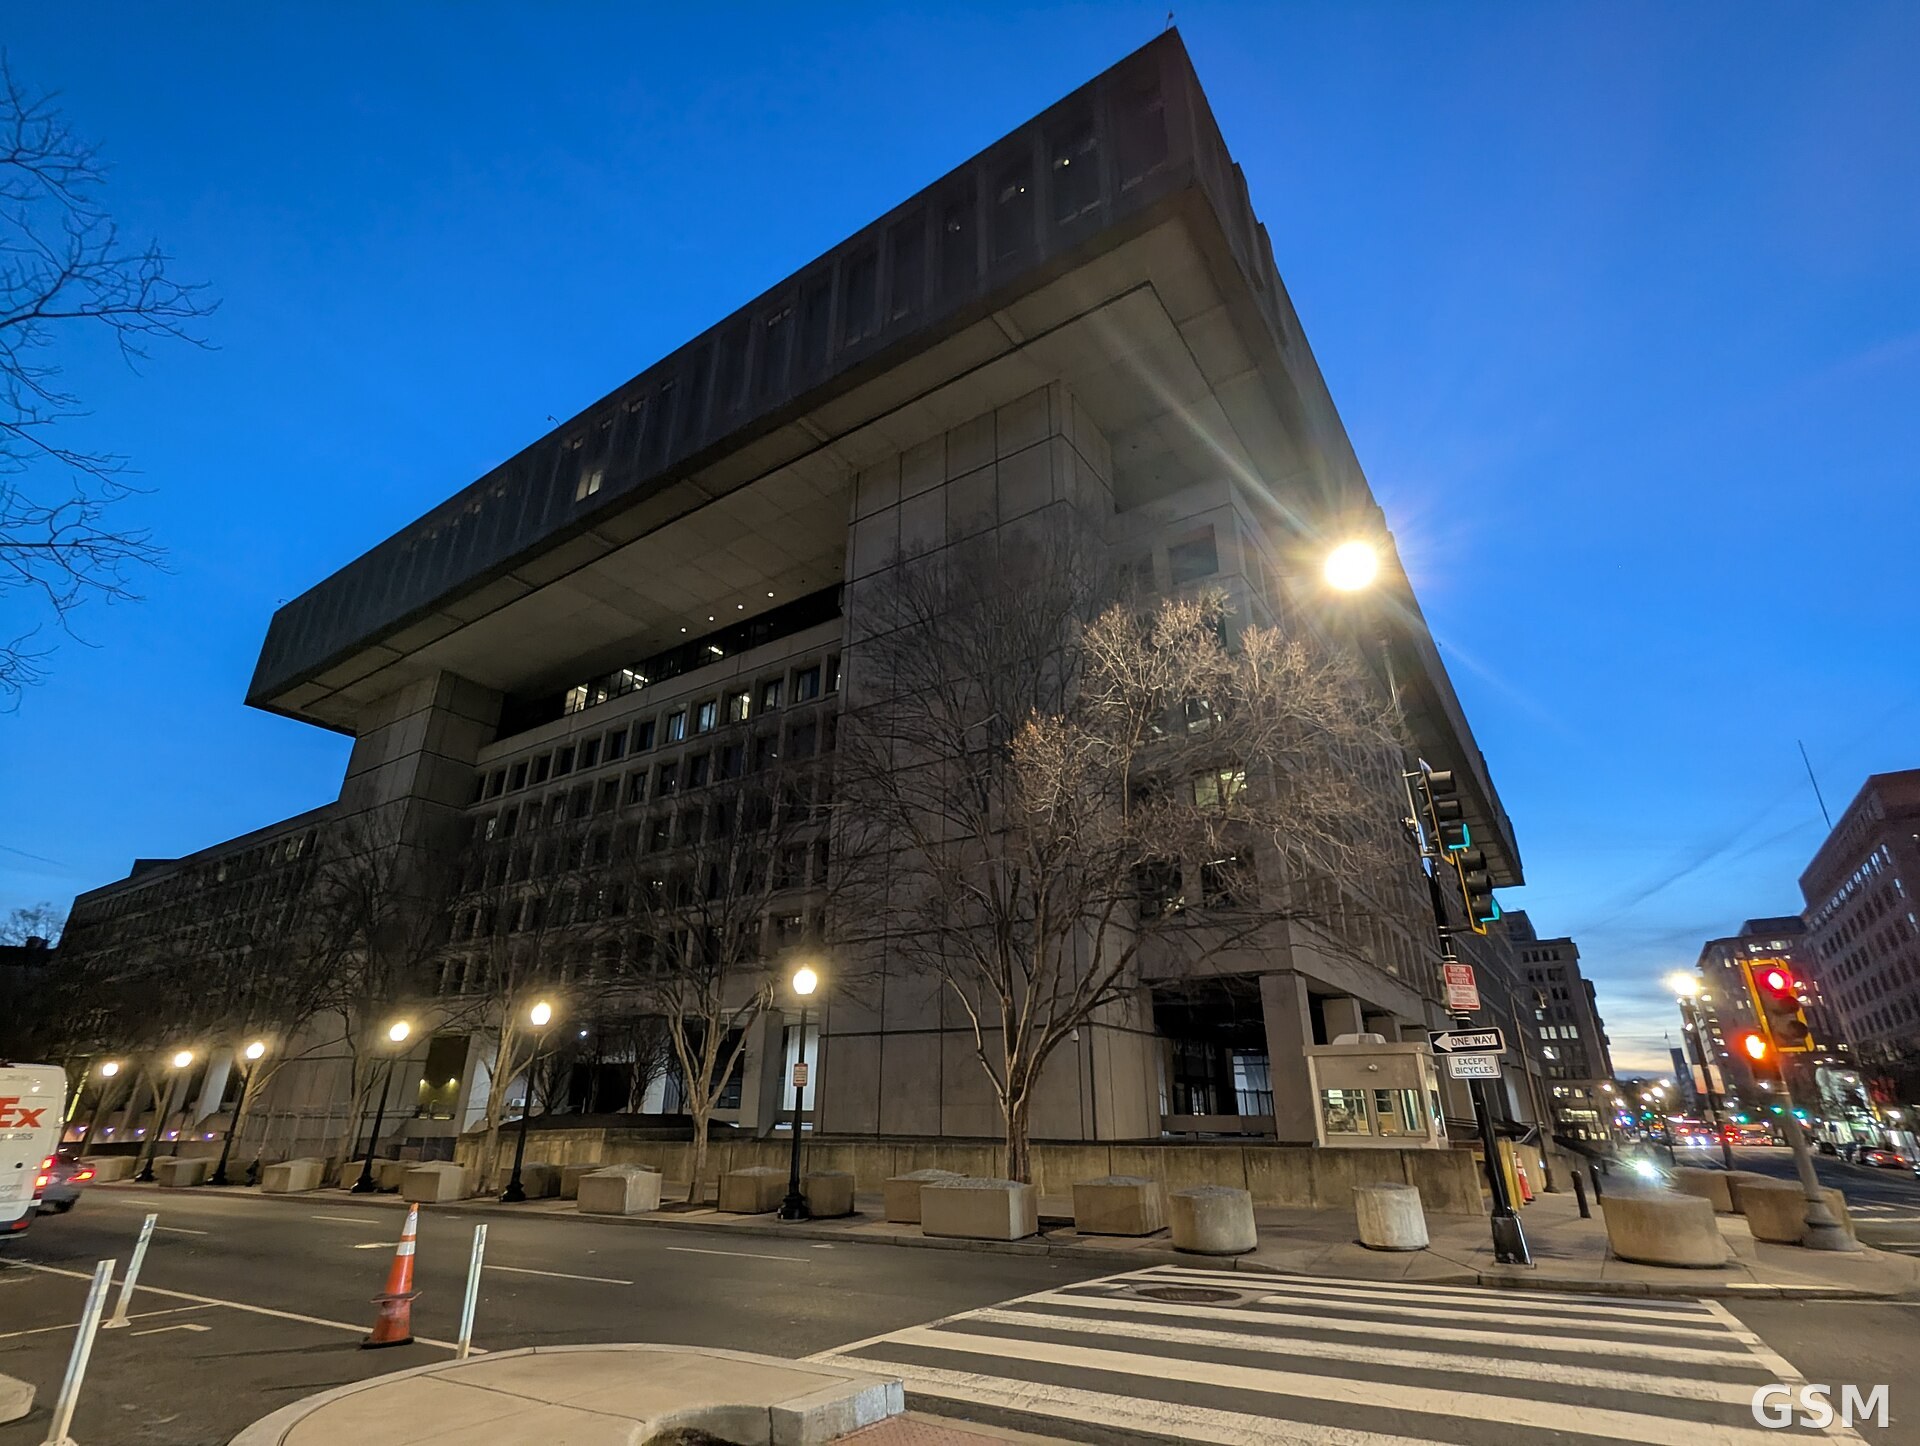
图片来源:图:位于华盛顿的联邦调查局总部 J. Edgar Hoover 大楼黄昏外景(资料图)。本案由联邦调查局 Dallas 外勤办公室调查、其网络司参与宣布查封。Sdkb 摄,CC BY-SA 4.0,经 Wikimedia Commons。 / Photo: The J. Edgar Hoover Building, FBI headquarters in Washington, D.C., at dusk (file photo). The case was investigated by the FBI's Dallas Field Office, and the FBI Cyber Division joined the announcement. Sdkb, CC BY-SA 4.0, via Wikimedia Commons.
GSM Global · 本篇英文版 English edition of this story